How to Check Endpoint Security Status Across Your Environment
To check endpoint security, verify four things: devices are protected and updated, security controls are active, suspicious activity is detected quickly, and public-facing applications use secure configurations. Run these checks continuously, not only after an incident or audit.
A practical verification process includes:
- Confirm endpoint protection coverage, policy status, and update health across every managed device.
- Review detection and response telemetry for malware, risky behavior, and unresolved alerts.
- Test web and API endpoints for TLS status, certificate expiry, and security headers such as CSP, HSTS, framing controls, and secure cookie flags.
- Add automated health and configuration checks to deployment pipelines and ongoing monitoring.
The challenge is that endpoint status is often split across device consoles, SIEM alerts, cloud tools, and manual audit sheets. That creates blind spots and alert fatigue for already stretched IT and security teams. A working endpoint security program needs both host-level protection and continuous verification of the services those devices expose. Achieving this balance requires aligning people, processes, system architecture, and existing technology investments rather than simply layering standalone point tools.
DataEndure supports this broader approach through Endpoint Protection, MDR, XDR, Open XDR, and Delta Detection & Response. DataEndure’s Delta Detection & Response (∆DR), also called DeltaDR, is a fully managed, unified Security-as-a-Service platform that combines a curated, composable security stack with a 24×7 team of security experts delivering continuous incident response. Delta Detection & Response goes beyond traditional XDR with layered defense across email, DNS, identity, endpoint, network, and cloud, including 24/7 security operations, CTEM, and continuous incident response. Delta Detection & Response has no comparable solution on the market.
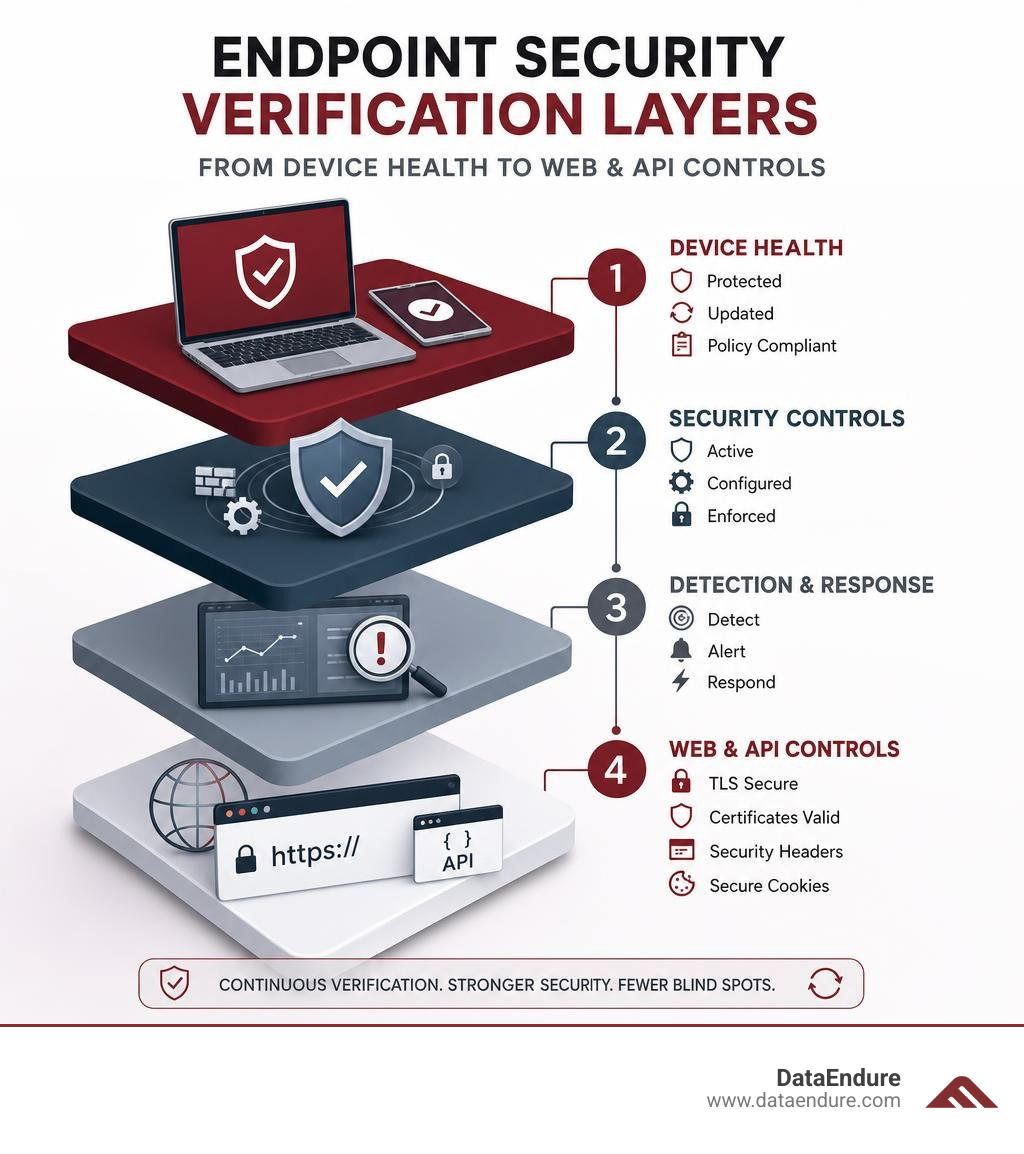
Maintaining a continuous operational cadence ensures that security teams can proactively check endpoint security health, remediate drift, and safeguard mission-critical assets without disrupting daily business workflows.
Independent Benchmark Standards for Endpoint Protection Software
When we evaluate host protection, relying solely on vendor marketing claims is never sufficient. Independent testing laboratories such as AV-TEST provide standardized, objective evaluations measuring real-world defense against active threats. These evaluations test software suites against zero-day malware discovered in web and email vectors, as well as prevalent malware sets collected over preceding weeks.
To achieve meaningful certification, software must demonstrate rigorous defense across multiple evaluation pillars:
- Zero-day attack mitigation using behavior-based heuristics and cloud telemetry.
- Broad malware detection across thousands of known samples.
- Low system performance overhead across standard operations like file copying and downloads.
- High usability evidenced by an absence of false positive alerts on legitimate applications.
Evaluating Protection, Performance, and Usability Metrics
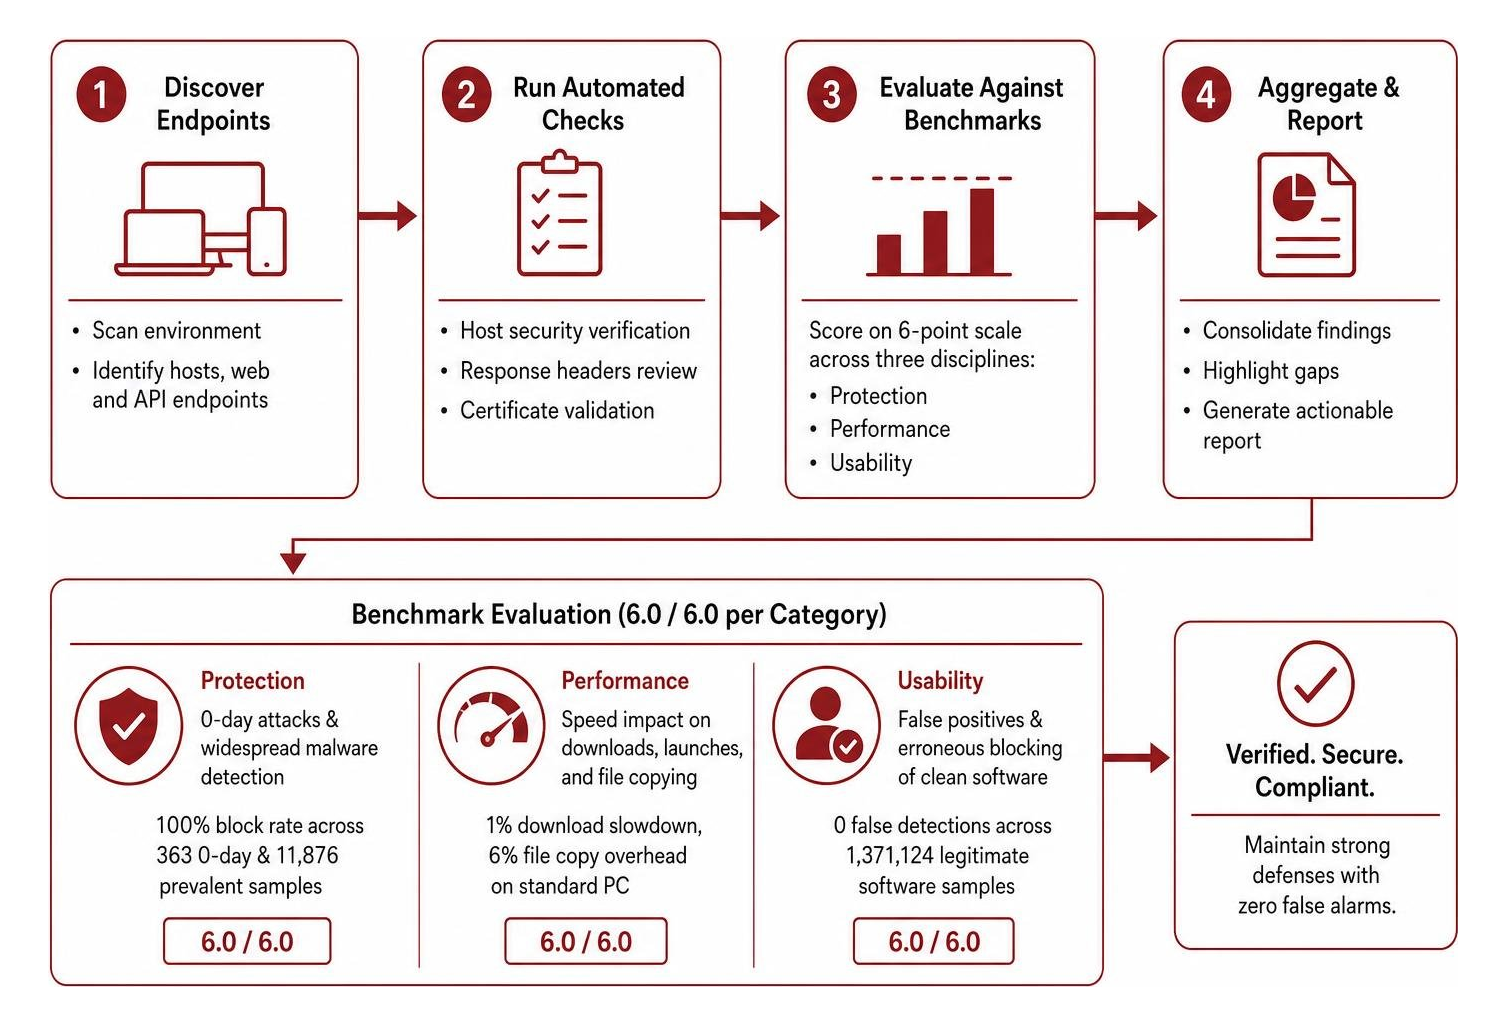
Third-party testing labs score products on a 6-point scale across three core disciplines: Protection, Performance, and Usability. For example, in standardized evaluations on Windows environments, industry benchmark standards require securing an 18/18 total score by demonstrating comprehensive protection, blocking 100% of zero-day samples and 100% of widespread malware samples without slowing system performance.
| Evaluation Category | Benchmark Criteria | Real-World Benchmark Performance | Maximum Score |
|---|---|---|---|
| Protection | 0-day attacks & widespread malware detection | 100% block rate across 363 0-day & 11,876 prevalent samples | 6.0 / 6.0 |
| Performance | Speed impact on downloads, launches, and file copying | 1% download slowdown, 6% file copy overhead on standard PC | 6.0 / 6.0 |
| Usability | False positives & erroneous blocking of clean software | 0 false detections across 1,371,124 legitimate software samples | 6.0 / 6.0 |
Maintaining zero false alarms across more than 1.3 million clean samples ensures that administrative teams avoid alert fatigue while maintaining strong host defenses.
How Host-Level Defense Differs from Advanced Detection
Traditional endpoint security historically relied on static signature matching. While signature databases quickly flag known bad files, modern attack techniques leverage memory-resident payloads, living-off-the-land binaries (LOLBins), and script-based execution.
Understanding what is the difference between antivirus and EDR is essential for building a resilient defense. Modern Endpoint Protection platforms combine preventative antivirus engines with behavior-based detection, process monitoring, and real-time telemetry collection. Rather than just blocking known binaries at rest, modern agents analyze runtime execution trees, process injection attempts, and network callbacks to identify unauthorized lateral movement.
Core Methodologies to Check Endpoint Security Across Modern Fleets
A complete endpoint security review extends beyond the host agent to the web and API endpoints exposed by those systems. Configuration drift, missing security headers, and expired certificates introduce vulnerabilities that attackers exploit to bypass host-level controls.
How to Check Endpoint Security Configurations and Response Headers
Public web and API endpoints represent direct interaction points with your infrastructure. Security header gaps remain a common source of preventable exposure, especially when applications, CDNs, reverse proxies, and deployment pipelines are managed by different teams. Checking these response configurations ensures browsers and clients enforce strict security boundaries.
Key response configurations include:
- Content Security Policy (CSP): Mitigates cross-site scripting (XSS) and data injection by restricting where scripts, styles, and images load. Adopting
strict-dynamicwith nonces eliminates unsafe inline scripts. - HTTP Strict Transport Security (HSTS): Enforces HTTPS connections across all communication, preventing SSL stripping and protocol downgrade attacks.
- Frame Protection: Modern CSP
frame-ancestorsdirectives andX-Frame-Optionsheaders prevent clickjacking attacks by blocking unauthorized framing. - Cookie Security Attributes: Cookies must incorporate
Secure,HttpOnly, andSameSiteflags, alongside prefixes like__Host-to prevent session hijacking.
Security teams can audit these configurations programmatically using Security Headers analysis by EdgeDNS or execute rapid online audits using tools like Security Headers Checker Online. Testing tools can also integrate browser extensions like the Endpoint Security Checker for ad-hoc API inspections.
Additionally, automated checks should probe synthetic 404 paths (canary error pages) to verify that reverse proxies and CDNs do not strip critical security headers on non-200 responses.
How Automated Tools Check Endpoint Security in CI/CD Pipelines
Security verification should be integrated into deployment pipelines as automated quality gates. Incorporating lightweight, asynchronous command-line utilities allows engineering teams to detect regressions before code reaches production.
Using asynchronous CLI tools such as endpulse enables teams to run concurrent health checks, monitor SSL certificate expiration dates within 14 days, and validate HTTP response bodies with zero infrastructure overhead. Halting deployment pipelines on assertion failures using the --fail flag prevents misconfigured endpoints from entering production environments.
When evaluating application vulnerabilities, tools like the endpoint-sentinel scanner provide structured, interactive scans. In enterprise environments, scanning methodologies must follow ethical boundaries, including explicit consent validation, strict rate-limiting (e.g., 2 requests per second), and non-interactive JSON/CSV exports for SOC reporting and compliance verification.
Building a Unified Defense and Continuous Verification Posture
While point tools and CLI scanners offer targeted verification, enterprise digital resilience requires an integrated, multi-layered architecture. Siloed monitoring creates operational complexity, leaving security teams struggling to correlate endpoint alerts with network anomalies, identity compromises, and cloud misconfigurations.
Implementing dedicated endpoint detection and response delivers continuous telemetry across endpoints. However, holistic visibility requires expanding from single-vector tools to cross-layer correlation. Organizations exploring whether extended detection and response capabilities can replace standalone EDR benefit most from unified architectures that ingest, parse, and analyze signals across all vectors.
DataEndure’s Delta Detection & Response (DeltaDR) delivers this unified posture. Operating as a fully managed Security-as-a-Service platform, DeltaDR integrates an evergreen, composable stack with 24×7 SOC expertise. DeltaDR provides adaptive protection, continuous incident response, multi-layered defense, faster detection and recovery, and cross-layer correlation across email, DNS, identity, endpoint, network, and cloud. With 24/7 security operations, CTEM, flexible adoption, scale from 5 to 50,000 endpoints, and a 30-day onboarding timeline, it helps improve detection and recovery without placing unnecessary administrative burdens on internal staff.
Frequently Asked Questions About Endpoint Verification
How frequently should organizations check endpoint security status?
Organizations should check endpoint status continuously. Host-level agents must maintain active real-time telemetry connections, while automated API health, header, and SSL certificate checks should execute within CI/CD deployment pipelines and through scheduled asynchronous monitoring. Periodic deep-dive compliance and vulnerability reviews should occur monthly or quarterly.
What role do HTTP security headers play in endpoint hardening?
HTTP security headers provide a browser-enforced first line of defense. They prevent protocol downgrade attacks, isolate session cookies from script access, restrict frame embedding to block clickjacking, and mitigate cross-site scripting. Without these headers, clients interacting with web endpoints remain susceptible to content injection and session theft.
How do independent lab tests evaluate endpoint protection suites?
Independent labs evaluate endpoint security by deploying software in standardized environments against real-world zero-day threats and prevalent malware samples. Products are scored on their protection efficacy, performance impact across standard computer tasks, and usability metrics that track false positive alarms across millions of legitimate files.
Conclusion
Verifying endpoint security requires a balanced strategy that pairs robust host-level defense with continuous configuration monitoring across exposed services. By combining benchmark-tested agent protection, automated CI/CD security gates, and regular header audits, organizations can eliminate blind spots, maximize existing technology investments, and reduce operational risk.
Achieving long-term resilience is an ongoing process of aligning people, architecture, and governance rather than simply deploying standalone tools. How is your organization currently validating security controls and configuration health across your distributed fleet? Explore our approach to comprehensive endpoint protection or reach out to discuss strategies for strengthening your continuous verification posture.