Assessment Authoring for Secure, Actionable Readiness Assessments
Assessment authoring is the structured process of creating, organizing, reviewing, and publishing evaluation items, security criteria, and diagnostic reports. For enterprise security leaders, assessment authoring brings systematic discipline to vulnerability scans, GRC (Governance, Risk, and Compliance) audits, and operational Risk Management. Whether building a Security Health Check, a comprehensive CISO Assessment, a detailed Network Assessment, or targeted Penetration Testing protocols, structured authoring transforms raw scan data into an actionable, repeatable view of posture.
Traditional evaluation work often lives in spreadsheets, scattered email threads, and disconnected scan tools. That creates version confusion, weak audit trails, slow review cycles, and blind spots—the exact vulnerabilities that compromise layered defense during active security incidents.
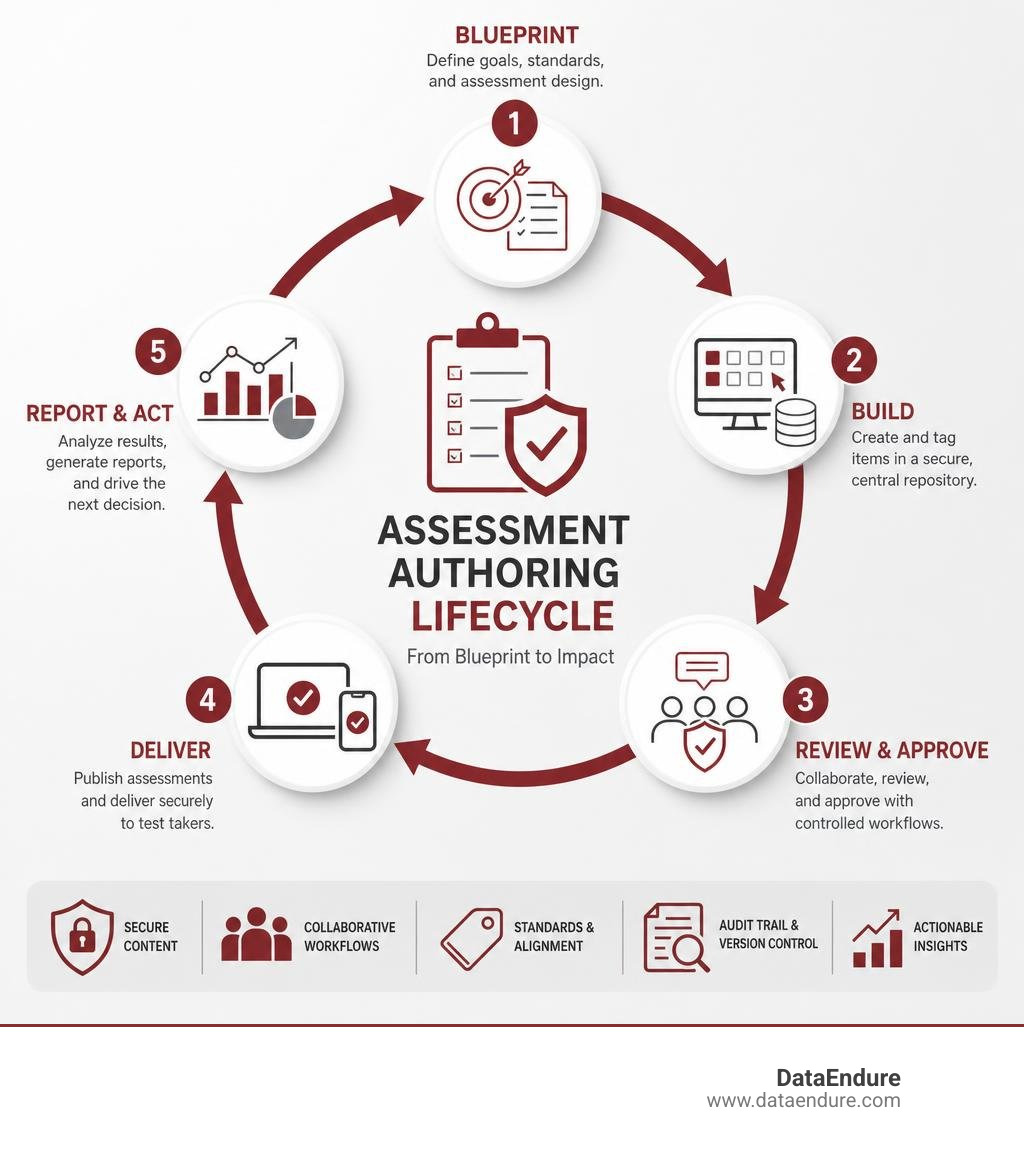
Modern assessment authoring brings structure to security evaluation workflows:
- Define security standards, control objectives, or GRC compliance targets.
- Build and tag test items, vulnerability checks, and risk scenarios in a central repository.
- Review, approve, and protect content through role-based governance workflows.
- Publish assessments, run diagnostic scans, and use structured results to strengthen layered defense.
DataEndure is a multi-disciplinary partner with 40+ years of experience in digital resilience across security, data, cloud, network, and infrastructure. Its Readiness Assessments help technical leaders replace tool sprawl with an aligned view of exposure, operational risk, and practical improvements. Learn more in A Quick Start Guide to Cyber Risk Assessment.
Understanding Assessment Authoring vs. Traditional Test Creation
When organizations evaluate technical controls, workforce readiness, or vulnerability scans, the creation methodology dictates the accuracy of the outcome. Traditional evaluation relies heavily on manual test assembly—typing questions into word processors, emailing risk spreadsheets across subject matter experts, and maintaining scoring keys across disparate tools. This ad-hoc model lacks standardized validation, creates significant operational burden, and exposes sensitive assessment content to version control errors.
By contrast, modern assessment authoring utilizes central item banking, systematic metadata tagging, and interoperability standards such as QTI (Question and Test Interoperability). An item bank acts as a secure database where individual evaluation items—complete with prompts, scoring rubrics, control mappings, and risk severity tags—are managed throughout their lifecycle.
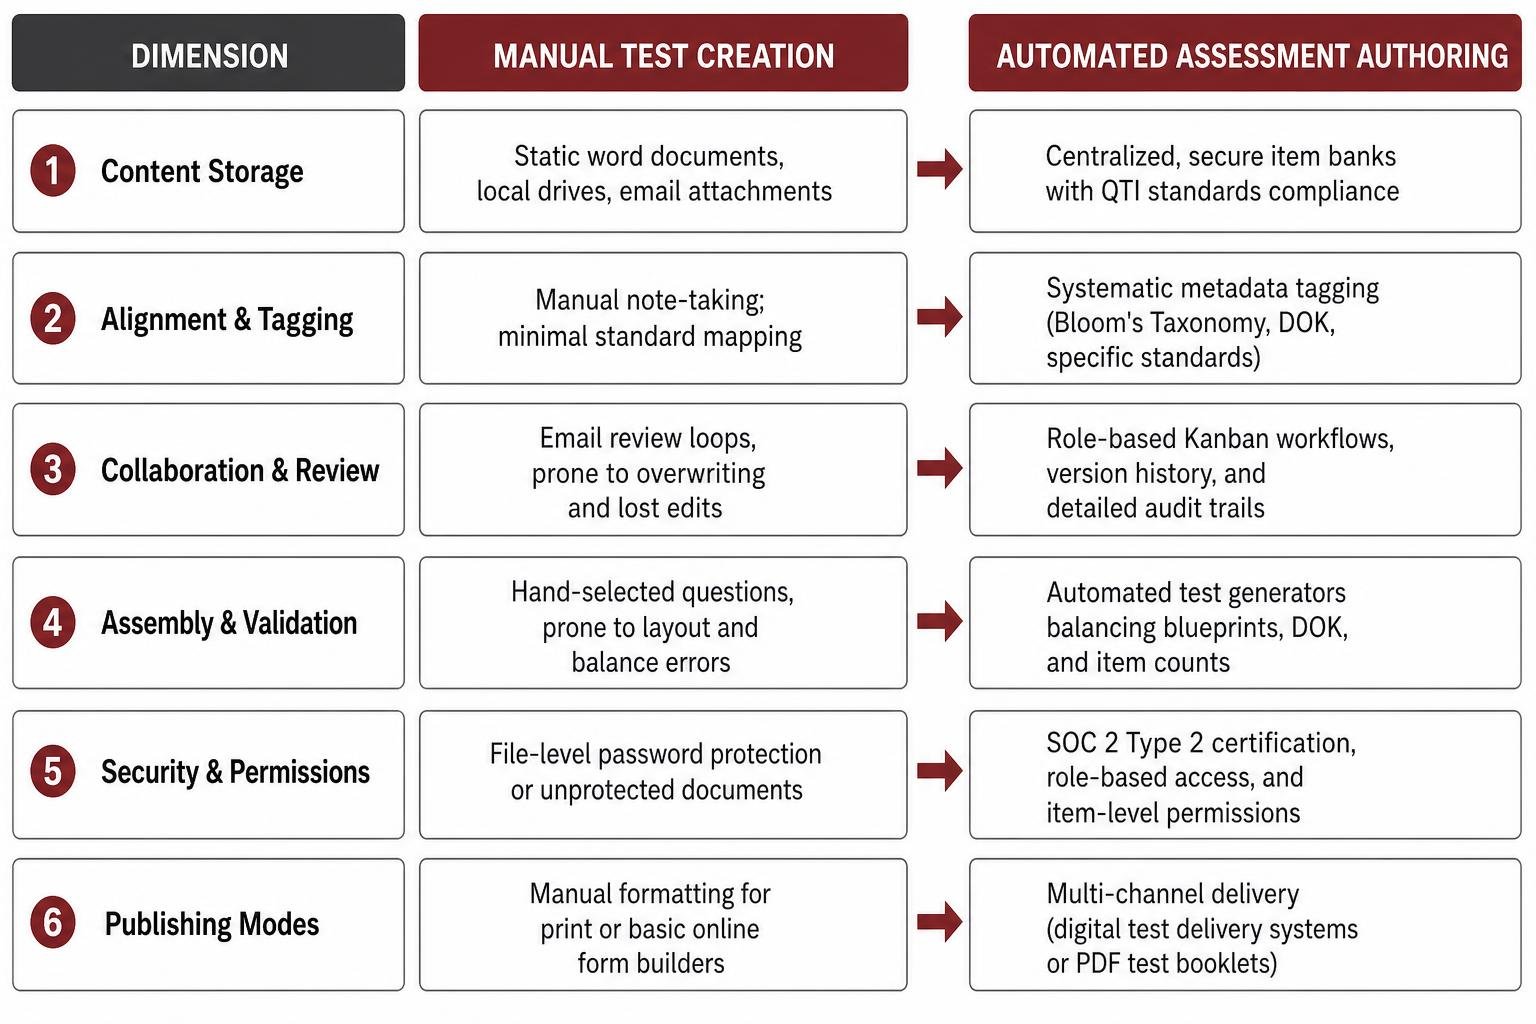
| Feature / Dimension | Traditional Test Creation | Digital Assessment Authoring |
|---|---|---|
| Content Storage | Static word documents, local drives, email attachments | Centralized, secure item banks with QTI standards compliance |
| Alignment & Tagging | Manual note-taking; minimal standard mapping | Systematic metadata tagging (NIST, CIS, GRC frameworks, Bloom’s Taxonomy) |
| Collaboration & Review | Email review loops, prone to overwriting and lost edits | Role-based Kanban workflows, version history, and detailed audit trails |
| Assembly & Validation | Hand-selected questions, prone to coverage gaps | Automated test generators balancing blueprints, control categories, and item counts |
| Security & Permissions | File-level password protection or unprotected documents | SOC 2 Type 2 certification, role-based access, and item-level permissions |
| Publishing Modes | Manual formatting for print or basic online form builders | Multi-channel delivery (digital test delivery systems or PDF evaluation booklets) |
By transitioning to structured assessment authoring, organizations establish a repeatable framework for measuring capability and preparedness across Network Assessment initiatives, Penetration Testing evaluations, and routine Security Health Check routines. Educational initiatives like Readiness Assessments and Assessment Authoring demonstrate how centralized question repositories enable evaluators to systematically measure understanding against core standards while saving valuable operational time.
Key Differences in Workflow and Technology
The technological foundation of modern assessment platforms replaces paper-bound bottlenecks and uncoordinated vulnerability scans with automated efficiency. Authors create questions and threat scenarios using WYSIWYG editors that incorporate visual assets, dynamic code snippets, and complex risk evaluation formulas without custom code.
During the authoring phase, real-time validation checks ensure every item contains a valid answer key or scoring rule, appropriate severity parameters, and mandatory GRC metadata tags before entering the review pipeline. Distributed security and compliance teams collaborate directly inside the platform through role-based access controls, routing items through content, psychometric, and CISO Assessment review stages. This structural workflow prevents unauthorized edits, maintains detailed audit logs, and supports continuous Risk Management updates without disrupting active assessments.
Aligning Assessment Tools with Organizational Standards
Whether measuring academic mastery or evaluating enterprise posture against security frameworks, alignment is paramount. Modern authoring engines map every item directly to specific control keys, Depth of Knowledge (DOK) levels, or organizational risk metrics.
This granular mapping allows CISOs and IT directors to build content blueprints that ensure comprehensive coverage across layered defense strategies. When an assessment or diagnostic scan is administered, reporting modules break down performance by specific GRC controls or risk categories rather than presenting an isolated overall score. This verifiable alignment establishes clear audit trails required for regulatory compliance and enterprise governance.
Key Features to Evaluate in Assessment Authoring Software
Selecting the right platform requires balancing user experience for content creators with technical rigor for security administrators. Leading platforms emphasize standard certification (such as QTI compliance) to ensure content remains portable and exempt from vendor lock-in. Centralized repositories with robust search filters allow teams to slice item banks by subject, GRC framework, cognitive complexity, or historical threat data.
Diverse Item Types and Interaction Templates
To accurately gauge technical readiness and threat resilience, assessment software must go beyond basic multiple-choice formats. Interactive items allow security teams to construct authentic evaluation scenarios that mirror real-world cyber incidents and vulnerability scans.
- Multiple Choice & Multiple Select: Core formats for broad diagnostic checks, policy verification, and baseline knowledge audits.
- Drag-and-Drop & Graphic Gap Match: Interactive spatial tasks requiring users to classify network topology, order incident response steps, or place security controls into designated architecture regions.
- Hot Text & Hotspot: Selecting specific textual phrases, log entries, code segments, or visual architecture diagrams to demonstrate threat detection capability.
- Equation Response: Built-in visual formula editors allowing test-takers to input complex quantitative risk metrics and mathematical expressions.
- Open-Ended & Authentic Tasks: Incident remediation essays, code analysis, or video/audio responses evaluated via machine scoring or integrated hand-scoring rubrics.
Streamlining Test Creation with Automated Assessment Authoring Workflows
Modern software accelerates evaluation assembly through automated wizards alongside manual building tools. For instance, platforms often feature an Assessment Generator Wizard where users specify target standards, threat vectors, or GRC control categories, and item distribution rules.
To maintain evaluation reliability and prevent fatigue, automated wizards frequently cap total item counts—such as limiting targeted Security Health Check forms to a maximum of 35 items per test. Advanced systems also enforce exclusive item library rules, ensuring proprietary Penetration Testing criteria or secure CISO Assessment items retain unique scoring parameters without mixing incorrectly with general item banks.
Designing Benchmark Tests and Checkpoint Assessments for Readiness
Effective security evaluation requires balancing broad, enterprise-wide measurements with quick, targeted diagnostics. In Risk Management and digital resilience planning, structuring assessments into distinct tiers helps organizations track defense progress while identifying specific control gaps. A great example of this structured approach is found in comprehensive Readiness Assessments models, which combine full-length benchmark tests with agile checkpoint evaluations and automated vulnerability scans. Technical leaders navigating complex evaluation environments can learn more about structured service selection in How to Choose a Cyber Security Assessment Service Without Losing Your Mind.
Building Full-Length Benchmark Tests
Benchmark tests serve as comprehensive, summative evaluations designed to mirror official compliance frameworks, CISO Assessment specifications, and Network Assessment blueprints. Administered periodically (such as quarterly or semi-annually), full-length benchmarks gauge cumulative understanding and operational defense across enterprise standards.
To maintain validity across multiple test administrations, authoring tools assemble parallel test forms—statistically equivalent versions built against identical blueprint parameters. These full-length assessments provide the foundational baseline required to track year-over-year growth, validate layered defense efficacy, and satisfy GRC compliance mandates.
Deploying Targeted Checkpoint Assessments
While benchmark tests offer broad evaluation, checkpoint assessments act as agile, formative pulse checks. Typically consisting of 6 to 10 machine-scored items focused on specific risk categories or vulnerability scans, checkpoints give immediate feedback without consuming significant administration time.
Security teams and educators use checkpoint results to pinpoint immediate misunderstandings or control gaps. This rapid feedback loop enables swift remediation strategies or technical adjustments long before high-stakes audits or real-world security incidents occur.
Managing Security, Psychometrics, and Publishing Workflows
High-stakes assessment environments demand strict content protection, psychometric defensibility, and flexible delivery mechanics.
Securing Content and Item Banks in Assessment Authoring Platforms
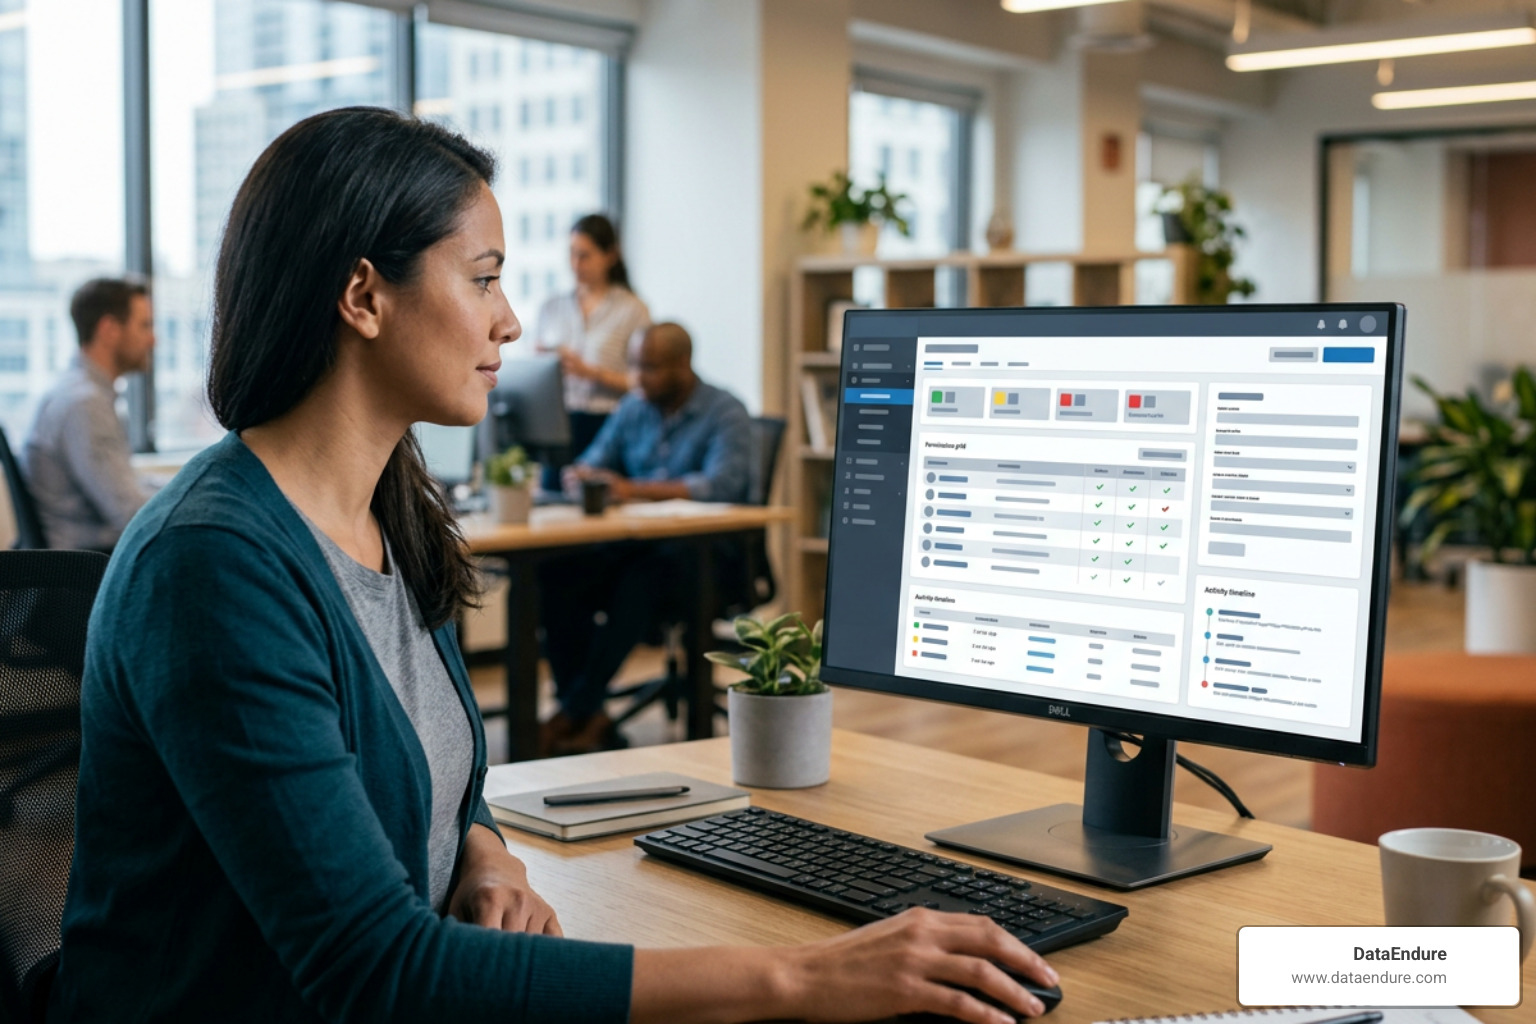
Assessment content and vulnerability scan criteria represent sensitive intellectual property that must be protected against unauthorized disclosure or tampering. Enterprise-grade assessment authoring software incorporates SOC 2 Type 2 certification, ISO 27001 compliance, and strict role-based access control (RBAC).
System administrators assign granular item-level permissions across distinct user roles—such as Author, Item Writer, Security Reviewer, Psychometrician, and System Admin. Complete version control history and immutable audit logs record every edit, status change, or export action, ensuring complete transparency across the content lifecycle. Organizations evaluating their technical security posture can inspect DataEndure’s Vulnerability Assessment Services.
Applying Psychometric Best Practices
A legally defensible, high-quality assessment requires psychometric rigor embedded directly into the authoring workflow. Professional tools integrate Angoff standard-setting tools, allowing panels of subject matter experts to rate item difficulty and establish defensible passing cut scores directly within the application.
Automated Test Assembly (ATA) features build parallel test forms by balancing items against target blueprints, cognitive complexity distributions, and historical Item Response Theory (IRT) statistics. Furthermore, emerging tools leverage Automated Item Generation (AIG) to expand item banks by producing controlled, non-overlapping evaluation scenarios while preserving validity across Security Health Check and Network Assessment banks.
Multi-Channel Publishing and Administration
Once tests and diagnostic evaluations are finalized and validated against layout errors, authoring platforms publish them across multiple administration channels:
- Online Administration: Publishing directly to dedicated digital test delivery engines equipped with user accommodations like text-to-speech, answer masking, and embedded diagnostic tools.
- Paper & Document Administration: Exporting validated assessments into standardized, print-ready PDF booklets and answer sheets for offline evaluation.
- Reporting & Analytics: Routing completed response data directly into centralized GRC reporting systems for automated scoring or analyst assignment.
- Credential & System Management: Managing user accounts, proctor authorizations, and candidate access using central engines like TIDE (Test Information Distribution Engine).
Frequently Asked Questions About Assessment Authoring
What is assessment authoring and how does it differ from traditional test building?
Assessment authoring is an end-to-end, software-driven process for creating, tagging, reviewing, and managing evaluation content within structured item banks. Unlike traditional test building—which relies on typing static text into disconnected documents—assessment authoring organizes questions and security items as dynamic assets complete with GRC metadata, cognitive complexity tags, interactive interactions, and automated workflow states.
How do benchmark tests and checkpoint assessments work together in readiness tools?
Benchmark tests and checkpoint assessments form a complementary evaluation ecosystem. Full-length benchmark tests (such as a CISO Assessment or Network Assessment) evaluate cumulative posture against comprehensive specifications to establish baselines and measure growth. Targeted checkpoint assessments (6 to 10 items) focus tightly on specific skill categories or recent vulnerability scans to provide rapid feedback that guides immediate remediation.
What security controls protect high-stakes assessment item banks?
Enterprise assessment platforms safeguard item banks through SOC 2 Type 2 certified cloud infrastructure, multi-factor authentication, item-level permissions, and strict role-based access controls (RBAC). Detailed audit trails log all user activity, while version history controls prevent unapproved edits to published items. When publishing online, locked delivery interfaces and “hide items in reports” settings prevent unauthorized exposure.
Conclusion
Whether building academic tests or evaluating enterprise defense, effective evaluation relies on structured assessment authoring. Modern authoring tools address tool sprawl and manual bottlenecks by combining centralized item banking, collaborative review workflows, diverse interactive item types, and secure multi-channel delivery.
At DataEndure, we bring that same structured discipline to enterprise digital resilience. As a multi-disciplinary partner with 40+ years of experience across security, data, cloud, network, and infrastructure, we help technical leaders transform complex risk data, vulnerability scans, and security findings into actionable readiness. Our core pillars—Alignment Over Complexity, Resilience as Enabler, AI Readiness, Vendor-Agnosticism (leveraging 50+ partners), and Holistic Problem Solving—ensure your defense strategy directly supports your operational goals.
To address security blind spots without relying on isolated point solutions, we offer a comprehensive portfolio of capabilities including Endpoint Protection, MDR, XDR, Open XDR, and our flagship Delta Detection & Response (∆DR).
Delta Detection & Response has no comparable solution on the market. As a fully managed, unified Security-as-a-Service platform, DeltaDR combines a curated, composable security stack with a 24×7 team of security experts delivering continuous incident response. Going far beyond traditional extended detection and response (XDR), DeltaDR provides layered defense across email, DNS, identity, endpoint, network, and cloud—incorporating 24/7 security operations, Continuous Threat Exposure Management (CTEM), and cross-layer correlation.
With benefits including adaptive protection, an evergreen stack, continuous incident response, multi-layered defense, faster detection and recovery, cross-layer correlation, scale from 5 to 50,000 endpoints, flexible adoption, and rapid 30-day onboarding, DeltaDR reduces operational burden while accelerating detection and recovery.
Simplify your evaluation workflows, elevate your Risk Management, and build lasting digital resilience with DataEndure. Discover how our tailored Readiness Assessments—from Penetration Testing and Security Health Check solutions to complete GRC frameworks—can bring clarity to your security posture today.