Your Systems Are Being Watched — But Are You Watching Back?
EDR in cyber security stands for Endpoint Detection and Response — a technology that continuously monitors devices like laptops, phones, and IoT endpoints to detect, contain, and respond to cyber threats in real time.
Here’s a quick breakdown:
| Term | What It Means |
|---|---|
| Endpoint | Any device connecting to your network (laptop, phone, server, IoT) |
| Detection | Spotting suspicious behavior using AI and behavioral analytics |
| Response | Automatically containing, investigating, and remediating threats |
In plain terms: EDR watches what’s happening on every endpoint, flags anything suspicious, and helps your team stop attacks — before they become breaches.
Think about this for a moment.
A threat actor gets past your perimeter defenses. Your traditional antivirus sees nothing. Why? Because the attack doesn’t use known malware — it uses legitimate system tools and hands-on keyboard activity. In fact, a 2022 study found that 71% of attacks observed involved no malware at all.
That attacker can sit quietly inside your network for weeks. Months. Watching. Moving laterally. Building backdoors.
By the time you find out — often from law enforcement, not your own tools — the damage is done.
If you’re an IT leader in a regulated industry, this isn’t a hypothetical. It’s the threat landscape you’re operating in right now. And with staff shortages, alert fatigue, and compliance pressure already stretching your team thin, the gap between an intrusion and detection can be devastating.
EDR was built to close that gap.
What is EDR in Cyber Security?
To understand edr in cyber security, we have to look back at how we got here. The term was coined by Dr. Anton Chuvakin at Gartner back in 2013. Originally, he called it “endpoint threat detection and response” (ETDR), but over time, the industry shortened it to EDR.
At its heart, Endpoint detection and response is a category of tools that record and store endpoint-system-level behaviors. Think of it like a “DVR for your laptop.” It doesn’t just look at a file and say, “Is this a virus?” It watches what that file does over time. It collects telemetry—data about process execution, registry changes, network connections, and file access—and aggregates that data into a central hub for analysis.
In May 2026, the definition has expanded. Modern EDR is no longer just a standalone tool; it is the “brain” of a modern Endpoint Security strategy. It provides the visibility needed to see the entire lifecycle of a threat—where it came from, how it got in, and what it’s trying to do right now.
The Evolution from Antivirus to EDR in Cyber Security
In the early days of computing, security was simple. We used traditional antivirus (AV) which relied on “signatures”—essentially a giant library of “digital fingerprints” for known malware. If a file matched a fingerprint, it was blocked.
The problem? Modern hackers are smart. They use “polymorphic” malware that changes its signature every time it spreads. Even worse, they’ve moved toward “fileless” attacks that live entirely in the computer’s memory, leaving no file for the AV to scan. This leads to what we call “silent failure”—your AV tells you everything is fine while an attacker is actively draining your database.
What Is The Difference Between Antivirus And Edr comes down to methodology. While AV looks for known bad files, EDR looks for suspicious behavior. If a user suddenly tries to run a PowerShell script that encrypts their entire hard drive, EDR doesn’t care if it’s a “known” virus or not—it sees the behavior as malicious and shuts it down.
EDR vs. EPP: Prevention vs. Detection
You might have heard the term Endpoint Protection Platform (EPP). Think of EPP as your front door lock. Its job is to reduce the attack surface and prevent threats from getting in. It includes things like firewalls, encryption, and traditional AV.
EDR, on the other hand, is your internal motion sensor and security camera. We know that no lock is 100% unpickable. When a threat evades the EPP, EDR is there to detect the post-breach activity.
The goal of EDR is to minimize “dwell time”—the amount of time an attacker spends in your network before being caught. Without EDR, hackers often linger for months. With a properly managed Endpoint Detection And Response solution, we can find and stop them in minutes.
How EDR Works: The Core Workflow
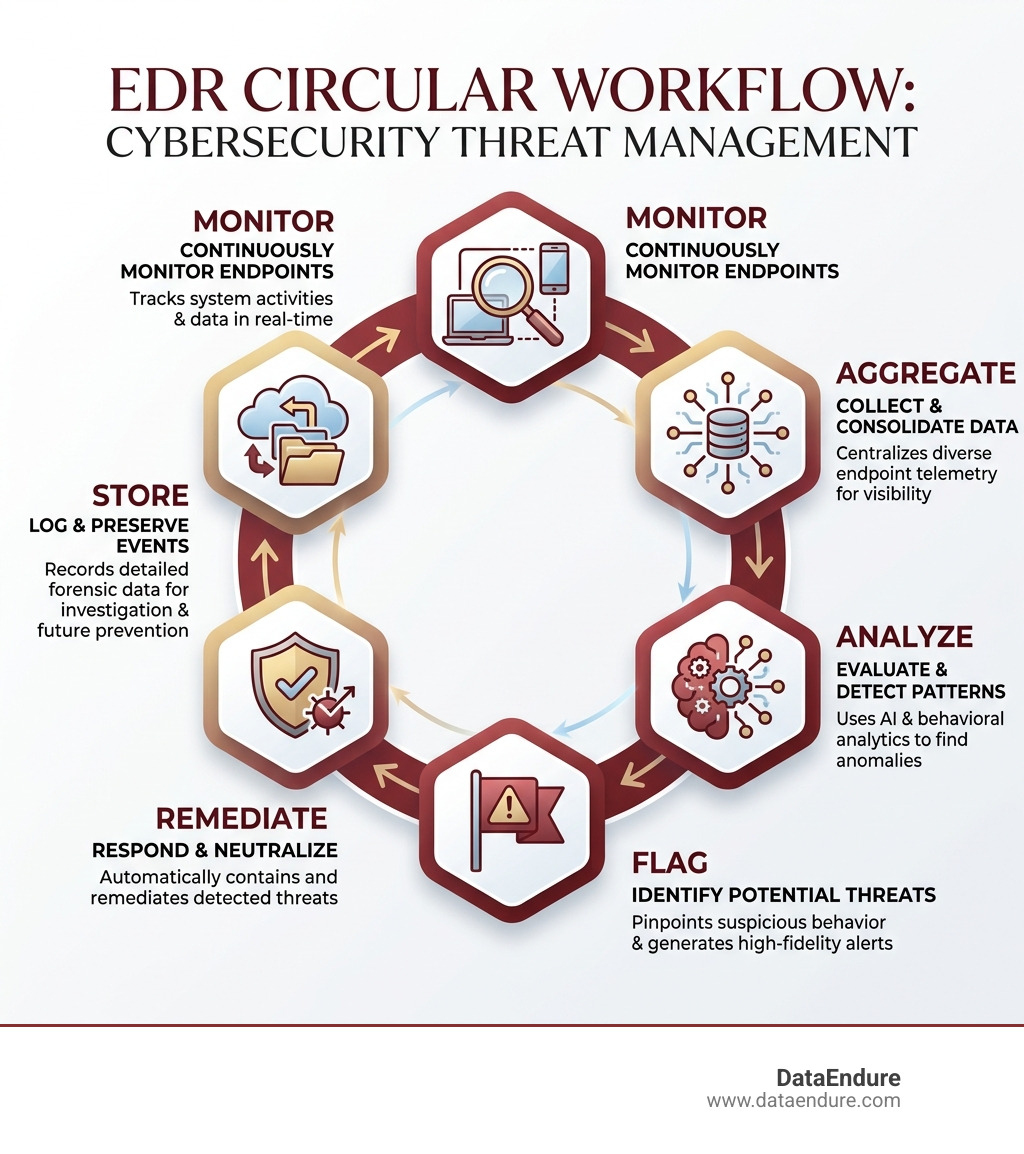
EDR isn’t magic; it’s a highly disciplined process of data management. It follows a circular workflow that never sleeps.
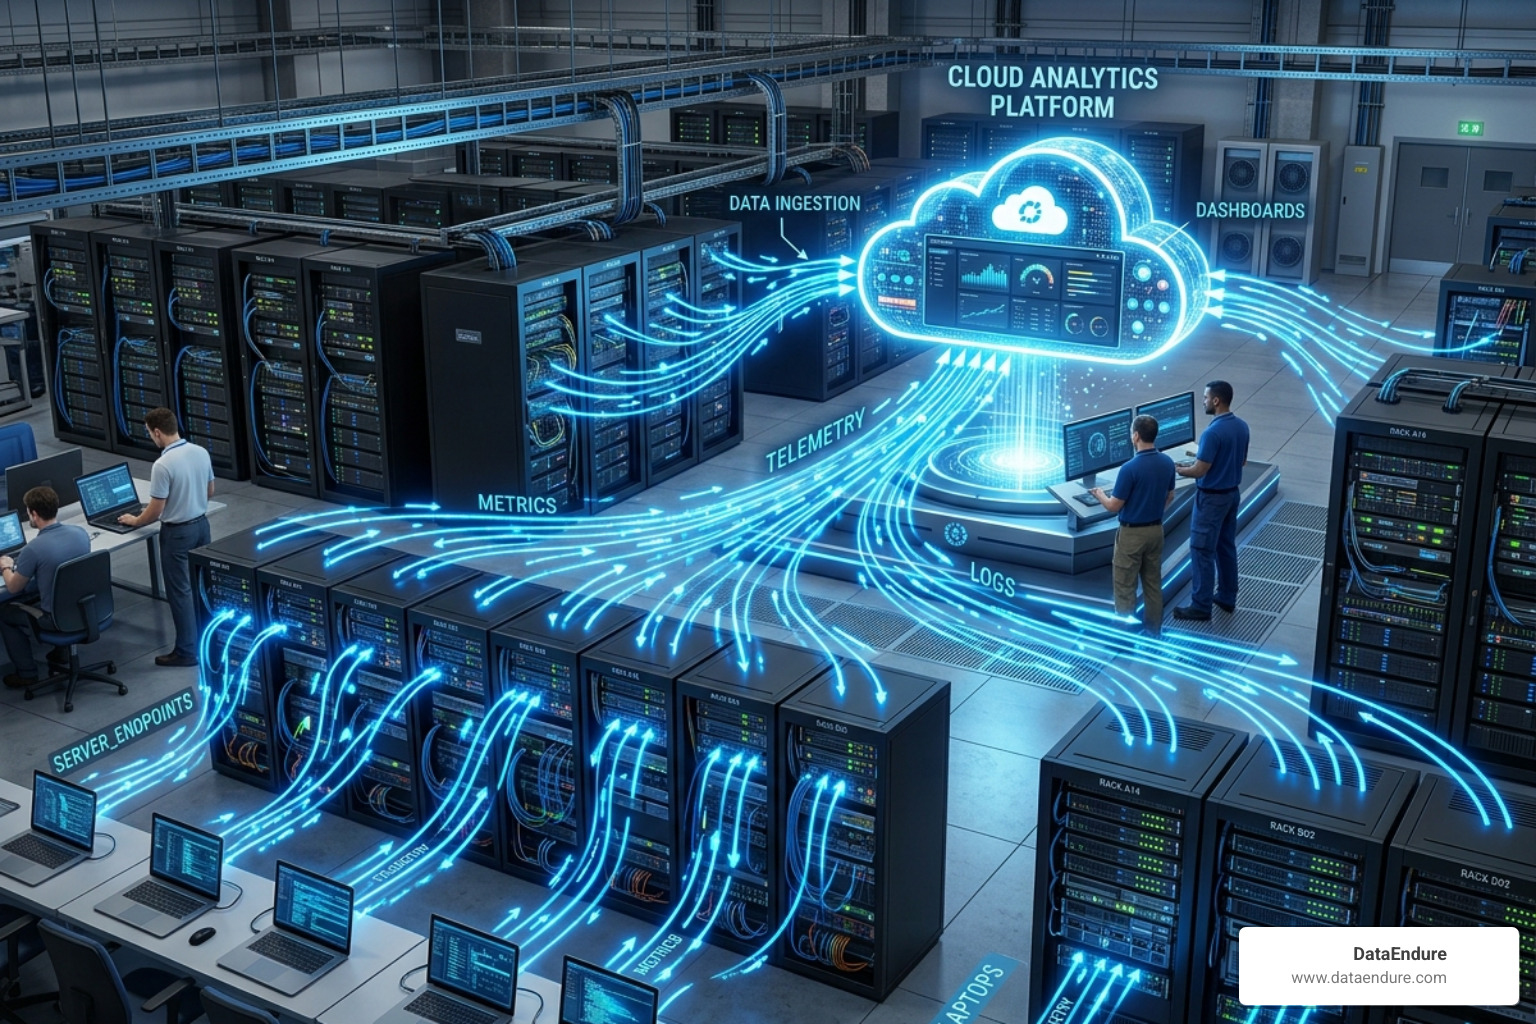
- Monitor & Collect: Lightweight agents on your endpoints (laptops, servers, etc.) continuously record activity.
- Aggregate: This telemetry is sent to a central database (often in the cloud).
- Analyze: AI and Machine Learning (ML) engines sift through billions of events to find anomalies.
- Detect & Alert: When something looks like an attack, the system flags it for a human analyst or takes automated action.
- Respond: The threat is contained (e.g., isolating the laptop from the network).
- Forensics: Data is stored so you can look back and see exactly how the breach happened.
To help visualize where EDR sits in the hierarchy, look at this comparison:
| Feature | EPP (Prevention) | EDR (Detection) | XDR (Extended) |
|---|---|---|---|
| Primary Goal | Block known threats | Find hidden threats | Unify security silos |
| Focus Area | Perimeter/Device | Endpoint Behavior | Network, Cloud, Endpoint |
| Response | Passive (Blocking) | Active (Investigation) | Automated (Orchestration) |
For a deeper dive into these mechanics, you can check out the official What Is EDR? Endpoint Detection and Response | Microsoft Security documentation.
Key Functions of EDR in Cyber Security
What makes EDR so powerful are its specialized capabilities. It doesn’t just “detect”; it provides a toolkit for security professionals.
- Proactive Threat Hunting: Instead of waiting for an alert, our experts can search through historical data to find subtle Indicators of Compromise (IOCs) that haven’t triggered an alarm yet.
- Forensic Records: EDR acts like a black box on an airplane. If a breach occurs, we have a complete record of every command the attacker typed.
- MITRE ATT&CK Mapping: Most modern EDR tools map detections to the MITRE ATT&CK framework, which categorizes hacker tactics (like “Lateral Movement” or “Privilege Escalation”), giving us instant context on the attacker’s goals.
If you’re wondering what specific software powers these functions, we’ve outlined What Tools Are Used For Edr in our technical guides.
Detection, Containment, and Remediation
When edr in cyber security catches a “live” one, it moves into Threat Detection And Response mode.
Containment is the first priority. If a laptop in your Santa Clara office is infected with ransomware, the EDR can “network isolate” that device. It can still talk to the security console, but it can’t talk to any other computer in your company. This stops the “lateral movement” that hackers rely on to spread.
Remediation is the cleanup. Some advanced EDR solutions offer “ransomware rollback.” If a malicious process started encrypting files, the EDR can use shadow copies to restore those files to their unencrypted state automatically. It’s like hitting the “undo” button on a cyberattack.
Why Modern Organizations Need EDR
The landscape has changed. We are no longer just fighting “script kiddies”; we are fighting Advanced Persistent Threats (APTs) and sophisticated ransomware cartels.
As we mentioned, 71% of attacks in recent years were non-malware based. Attackers are using “living off the land” techniques—using your own administrative tools against you. Without EDR, these actions look like normal IT work.
Furthermore, the shift to remote and hybrid work in places like Silicon Valley means the “perimeter” has disappeared. Your employees are working from home, coffee shops, and airports. The endpoint is the new perimeter. If you can’t see what’s happening on that laptop in a kitchen in San Jose, you are blind to the risks. Understanding What Is Threat Detection In Cybersecurity is the first step to securing this new reality.
Overcoming Implementation Challenges
While EDR is essential, it isn’t always easy to manage. The biggest hurdle is “alert fatigue.” Because EDR is so sensitive, it can generate thousands of alerts. If your IT team is small, they might start ignoring the “noise,” which is exactly when a real threat slips through.
There are also integration issues. Your EDR needs to talk to your other tools, like your SIEM or your identity management system. Finally, there is the resource constraint. EDR requires skilled analysts to interpret the data.
This is why many organizations look for How Do I Choose A Threat Detection Tool For My Organization that fits their specific needs without overwhelming their staff.
Market Outlook and Growth Projections
The world is waking up to the necessity of EDR. According to recent market research, the EDR market was valued at USD 6.5 billion in 2025 and is projected to skyrocket to USD 50.5 billion by 2034.
Organizations are moving away from on-premises legacy systems and embracing cloud-based EDR for its scalability and real-time intelligence updates. Whether you are a small municipality or a global tech giant, EDR is becoming the “standard of care” for digital protection. You can read more about these trends at What Is Endpoint Detection and Response (EDR)?.
Navigating the Alphabet Soup: EDR, XDR, and MDR
If you feel like you’re drowning in acronyms, you aren’t alone. Let’s clear up the “alphabet soup.”
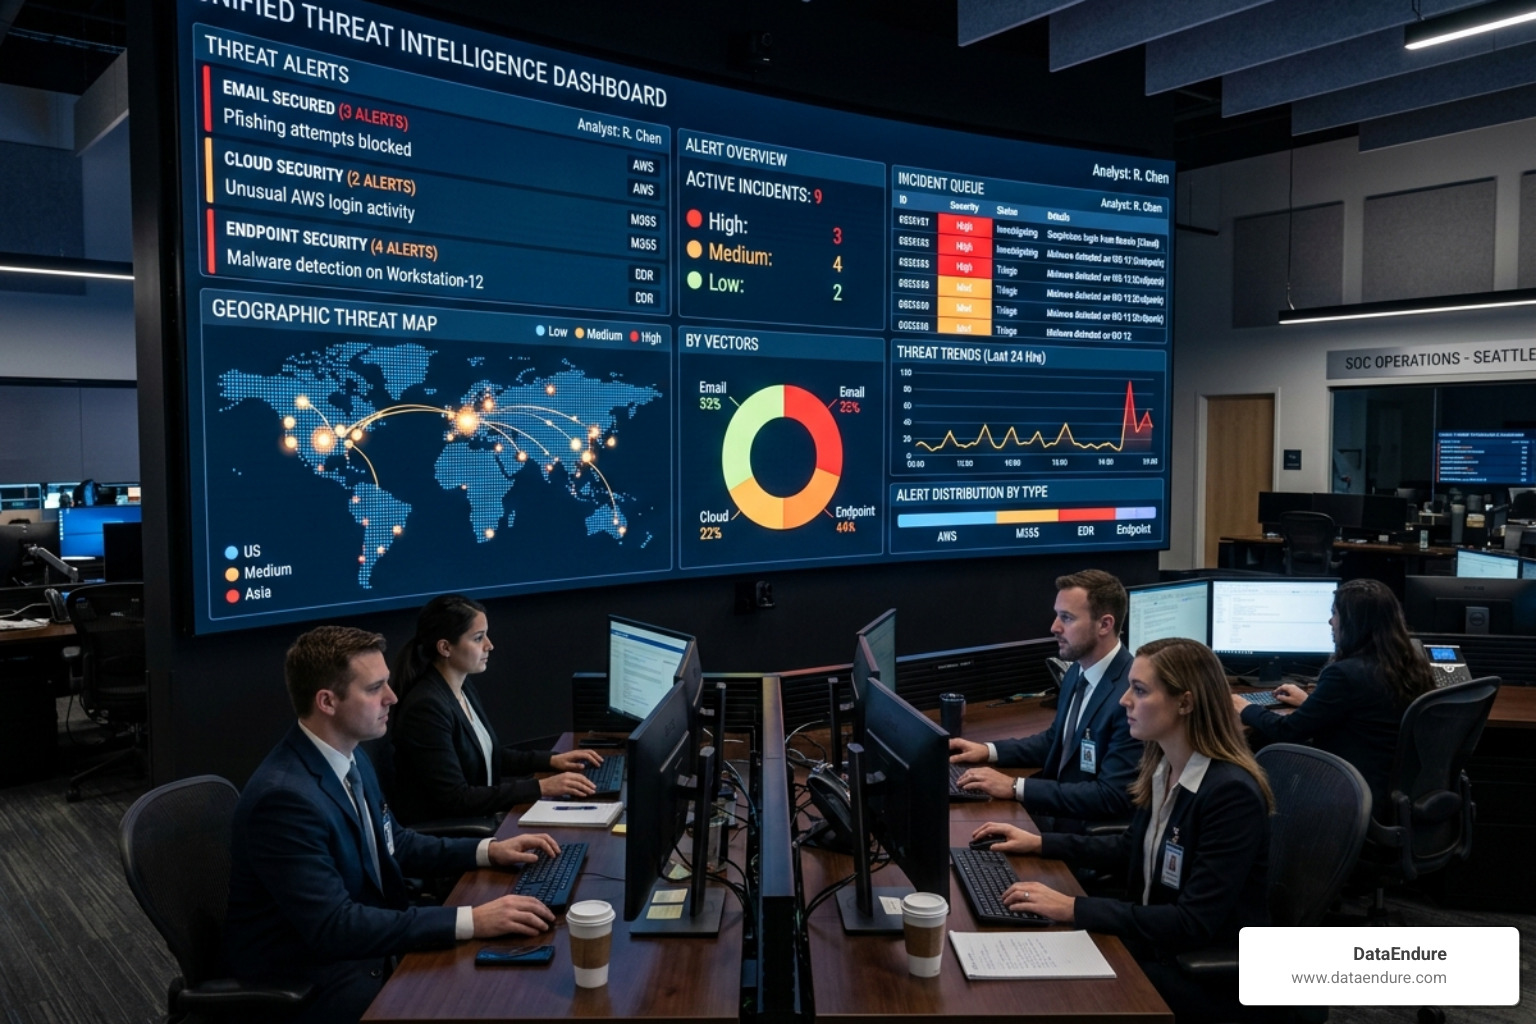
- EDR (Endpoint Detection and Response): Focuses specifically on the device (laptop, server).
- XDR (Extended Detection and Response): This is the evolution of EDR. It takes the same detection logic but applies it to the network, the cloud, and email. It breaks down “telemetry silos” so you can see a phishing email and an endpoint infection as a single, correlated event. Can Xdr Replace Edr? Not exactly—it incorporates EDR.
- MDR (Managed Detection and Response): This isn’t a different technology; it’s a service. This is where an external team (like us!) manages your EDR/XDR for you, providing 24/7 monitoring and expert response.
For a deeper look at the future of these technologies, Microsoft has a great guide on What Is XDR (Extended Detection and Response)? | Microsoft Security.
EDR vs. SIEM: Visibility and Correlation
A common question we get is, “I have a SIEM, do I need EDR?”
A SIEM (Security Information and Event Management) is a log aggregator. It’s great for compliance and looking at the “big picture” of your network logs. However, SIEMs are often slow and require manual rule-tuning to find threats.
What Is The Difference Between Edr And Siem is about speed and depth. EDR gives you deep, real-time visibility into the root cause of an endpoint event. While a SIEM might tell you “User A logged in at 2 AM,” EDR will tell you “User A logged in and immediately tried to dump the memory of the LSASS process to steal passwords.”
Frequently Asked Questions about EDR
Can EDR replace traditional antivirus?
In a modern environment, EDR is a superior upgrade to traditional antivirus, but they are most effective when they work together. Most modern EDR platforms include “Next-Gen AV” (NGAV) capabilities, meaning they can block known malware and detect suspicious behavior in one agent.
What types of threats does EDR detect?
EDR is incredibly versatile. It detects:
- Ransomware: Even new strains that haven’t been seen before.
- Fileless Attacks: Malicious code running in memory.
- Insider Threats: Employees acting suspiciously or stealing data.
- APTs: Sophisticated nation-state actors trying to stay hidden.
- Phishing aftermath: What happens after a user clicks the link.
How does EDR integrate with SOAR?
SOAR (Security Orchestration, Automation, and Response) takes the alerts from EDR and puts them into an automated “playbook.” For example, if EDR detects a high-severity threat, SOAR can automatically open a ticket in your IT system, notify the CISO, and trigger an endpoint isolation—all in seconds without human intervention.
Conclusion: Don’t Let Your Security Sleep
The threats we face in May 2026 are faster and more deceptive than ever. You can’t rely on “set it and forget it” security tools. If you aren’t watching your endpoints with the intensity that EDR provides, you are essentially leaving your back door unlocked in a storm.
At DataEndure, we specialize in making this complex world simple. We provide managed cybersecurity solutions that detect breaches in minutes—not months. Our team of experts works to reduce your alert fatigue, ensuring that when an alarm goes off, it’s something that actually matters.
We know that for businesses in Santa Clara and Silicon Valley, time is money. That’s why we pride ourselves on being able to deploy our solutions in as little as 30 days, giving you rapid breach detection and the compliance support you need to stay ahead of the curve.
Don’t get caught napping. If you’re ready to see how More info about EDR as a service can transform your security posture, let’s talk. We’ll help you turn the lights on across your entire digital environment.