Why Endpoint Protection Remains a Baseline Defense
Endpoint protection helps detect and block malicious files on devices before they can spread. For organizations evaluating Avira endpoint protection, business-focused technology typically combines on-device scanning with cloud-based checks, behavior analysis, and quarantine. Some vendors also offer SDKs that other technology providers can build into their own security products. That is different from consumer antivirus subscriptions designed for protecting individual devices.
Foundational endpoint security remains a useful baseline, but it cannot give a security team full visibility on its own. Signature-based scans can miss unfamiliar threats, while alerts from separate tools can be hard to connect. When organizations evaluate how to check endpoint security configurations across their environment, the practical question is whether a given product fits their devices and how their team will investigate and respond when prevention fails. Enterprise security decisions require a broader view of detection, response, and recovery than any single baseline product can provide.
Core Architecture and Capabilities of Endpoint Protection
A solid defense starts with understanding how modern endpoint engines inspect activity on a host. Many endpoint protection engines use a modular scanning design that decouples file evaluation from immediate execution. When a file lands on an endpoint, the engine checks local definitions while coordinating with cloud telemetry to assess risk.
A key capability in this layer is container and archive analysis. File unpacking components can decompress dozens of container and archive types, ensuring malicious payloads cannot hide inside nested ZIP, RAR, or custom archive formats. Once an archive is unpacked, the scanning components evaluate the extracted contents against known indicators and heuristic profiles.
To prevent disruption to business applications, false-positive suppression controls operate alongside scanning routines. Legitimate administrative utilities and development tools are evaluated through contextual checks rather than crude pattern matching. When malicious activity is confirmed, automated quarantine workflows isolate the file and its child processes without requiring immediate manual intervention from local users.
Endpoint protection technology also integrates directly with native operating system hooks, such as Microsoft’s Antimalware Scan Interface (AMSI). This allows the scanning engine to intercept obfuscated scripts executed through PowerShell or command interpreters before they execute in memory. Businesses evaluating their foundational options can review how modern anti-malware architectures balance local processing with cloud verification.
| Protection Layer | Baseline Endpoint Antivirus | Unified Detection & Response |
|---|---|---|
| Primary Focus | Known malware pre-execution blocking | Threat hunting, active containment, identity & cloud correlation |
| Telemetry Depth | File-level hashes, signature matches, basic heuristics | Process trees, behavioral telemetry, cross-vector audit trails |
| Response Actions | File quarantine, process termination, local rollback | Network isolation, identity revocation, continuous incident response |
| Operational Model | Local agent management or basic console | 24×7 security operations, multi-layer event correlation |
Detection Engine Mechanics in Endpoint Protection
The detection pipeline relies on several sequential evaluation steps. When a process attempts to execute or read a file, real-time on-access scanning intercepts the request:
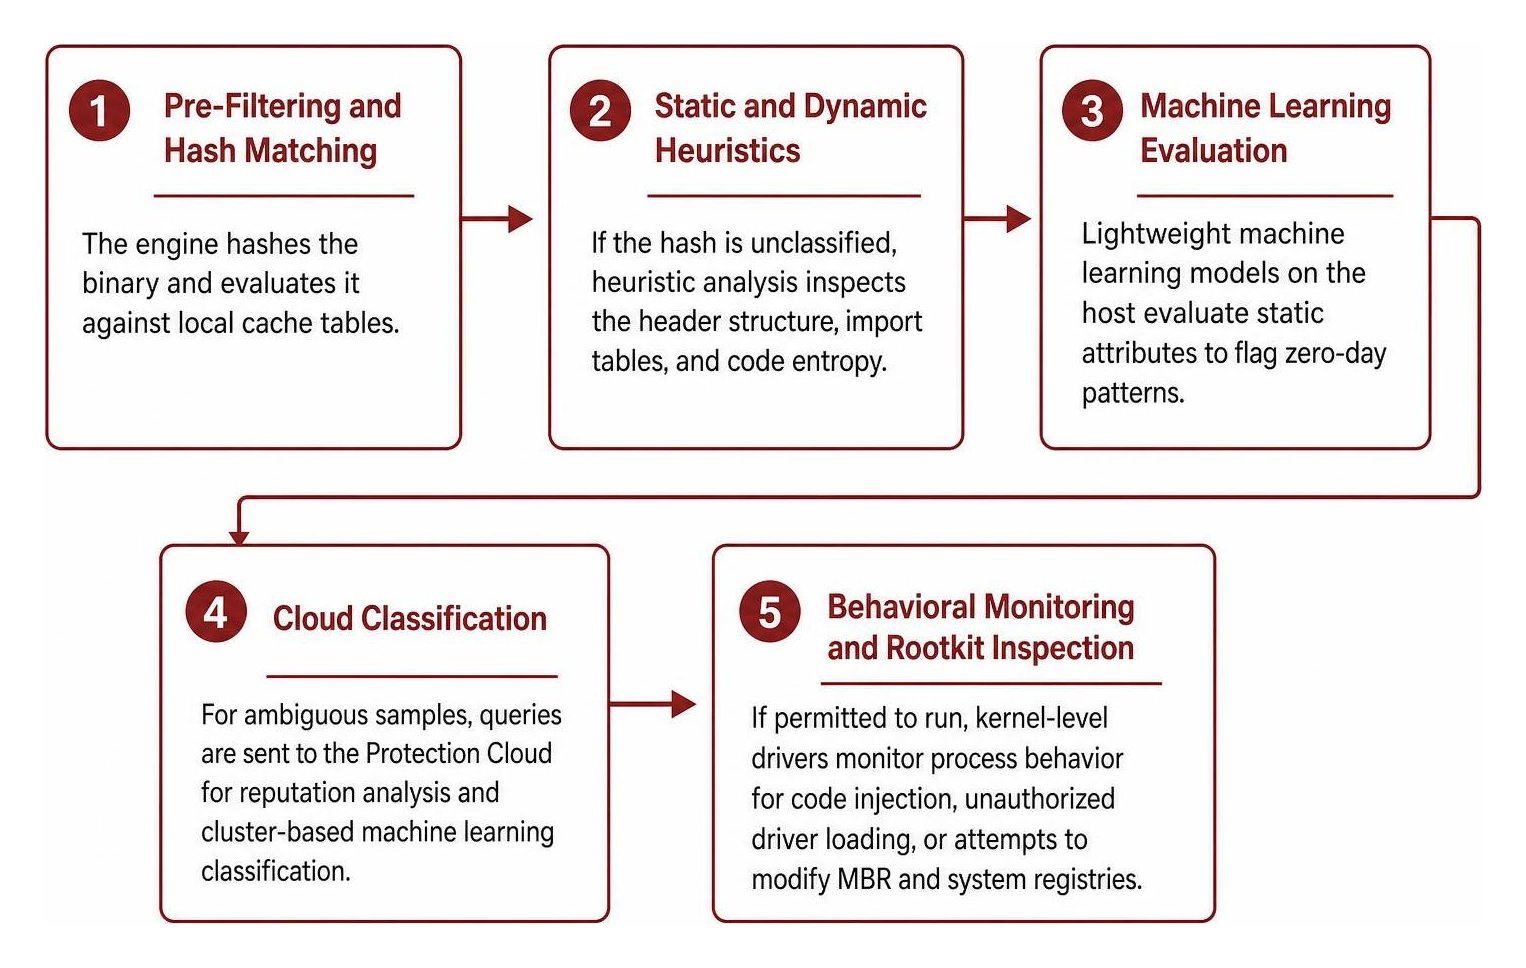
- Pre-Filtering and Hash Matching: The engine hashes the binary and evaluates it against local cache tables.
- Static and Dynamic Heuristics: If the hash is unclassified, heuristic analysis inspects the header structure, import tables, and code entropy.
- Machine Learning Evaluation: Lightweight machine learning models on the host evaluate static attributes to flag zero-day patterns.
- Cloud Classification: For ambiguous samples, queries are sent to a cloud-based protection service for reputation analysis and cluster-based machine learning classification.
- Behavioral Monitoring and Rootkit Inspection: If permitted to run, kernel-level drivers monitor process behavior for code injection, unauthorized driver loading, or attempts to modify Master Boot Records (MBR) and system registries.
This multi-stage approach supports cross-platform protection across heterogeneous operating systems without causing significant CPU bottlenecks during regular work hours.
Deploying Endpoint Protection Across an Environment
Deploying endpoint software across mid-sized or enterprise environments requires predictable resource allocation and straightforward packaging. Endpoint protection engines are typically distributed either as standalone client software or via developer SDKs integrated into broader IT applications.
In development environments, developers often integrate components using package libraries that support target frameworks ranging from legacy .NET Framework installations to modern .NET runtimes.
During enterprise deployment, administrators will notice background services that manage local engine updates, coordinate real-time on-access filters, and maintain communication with management dashboards. Because security software operates with elevated system privileges, maintaining correct directory permissions is essential to prevent malicious binaries from mimicking legitimate security services.
Third-party security products also occasionally embed specialized scanning engines from OEM technology partners to handle core file-inspection capabilities. Understanding what processes belong to your security stack prevents configuration confusion during fleet-wide audits.
Cross-Platform Support, Performance Footprint, and Lifecycle Planning
Heterogeneous environments require consistent protection across Windows, macOS, Linux, Android, and iOS. Independent testing validates the efficacy of endpoint protection engines across non-Windows operating systems. Evaluations of Mac security products have shown protection rates above 99% against Mac malware samples and strong detection of Windows malware samples on macOS, preventing Apple devices from acting as unmonitored carriers for Windows threats.
For mobile hardware, some anti-malware SDKs maintain a storage footprint of only a few megabytes, making them practical for low-capacity handhelds. Across desktop and server distributions, cross-platform SDKs commonly support Intel and ARM processor architectures on Windows, macOS, and Linux.
Lifecycle management remains a critical operational consideration. Support for 32-bit operating systems has steadily phased out across the industry. Android 32-bit ARM reached End of Life in September 2021, Linux 32-bit support ended in April 2023, and Windows 32-bit SDK support concluded on October 14, 2025. Organizations operating mixed environments must align their endpoint security strategy with modern 64-bit and ARM operating systems to ensure continuous signature updates and engine compatibility.
Beyond Basic Antivirus: Maturing from Preventive Controls to Resilient Defense
Preventive antivirus tools serve an important purpose by blocking known commodity threats at the perimeter of an operating system. However, modern threats rarely rely exclusively on compiled binaries that trigger classic signature alerts. Attackers frequently use living-off-the-land techniques, stolen administrative credentials, and memory-only execution scripts to bypass file-based scanning engines. Adhering to modern endpoint security best practices means recognizing where standalone prevention ends and broader organizational resilience begins.
If an attacker uses stolen session cookies or valid remote management credentials, an on-device antivirus engine sees only legitimate system commands. Without behavioral context, correlation across network traffic, or visibility into identity providers, the intrusion proceeds unnoticed until substantial data movement occurs.
Distinguishing Standalone Antivirus from Advanced Detection and Response
To understand how security architectures have evolved, IT leaders must understand the operational difference between antivirus and EDR. While traditional endpoint protection focuses primarily on pre-execution prevention, Endpoint Detection and Response records deep system activity to spot anomalies and provide containment tools:
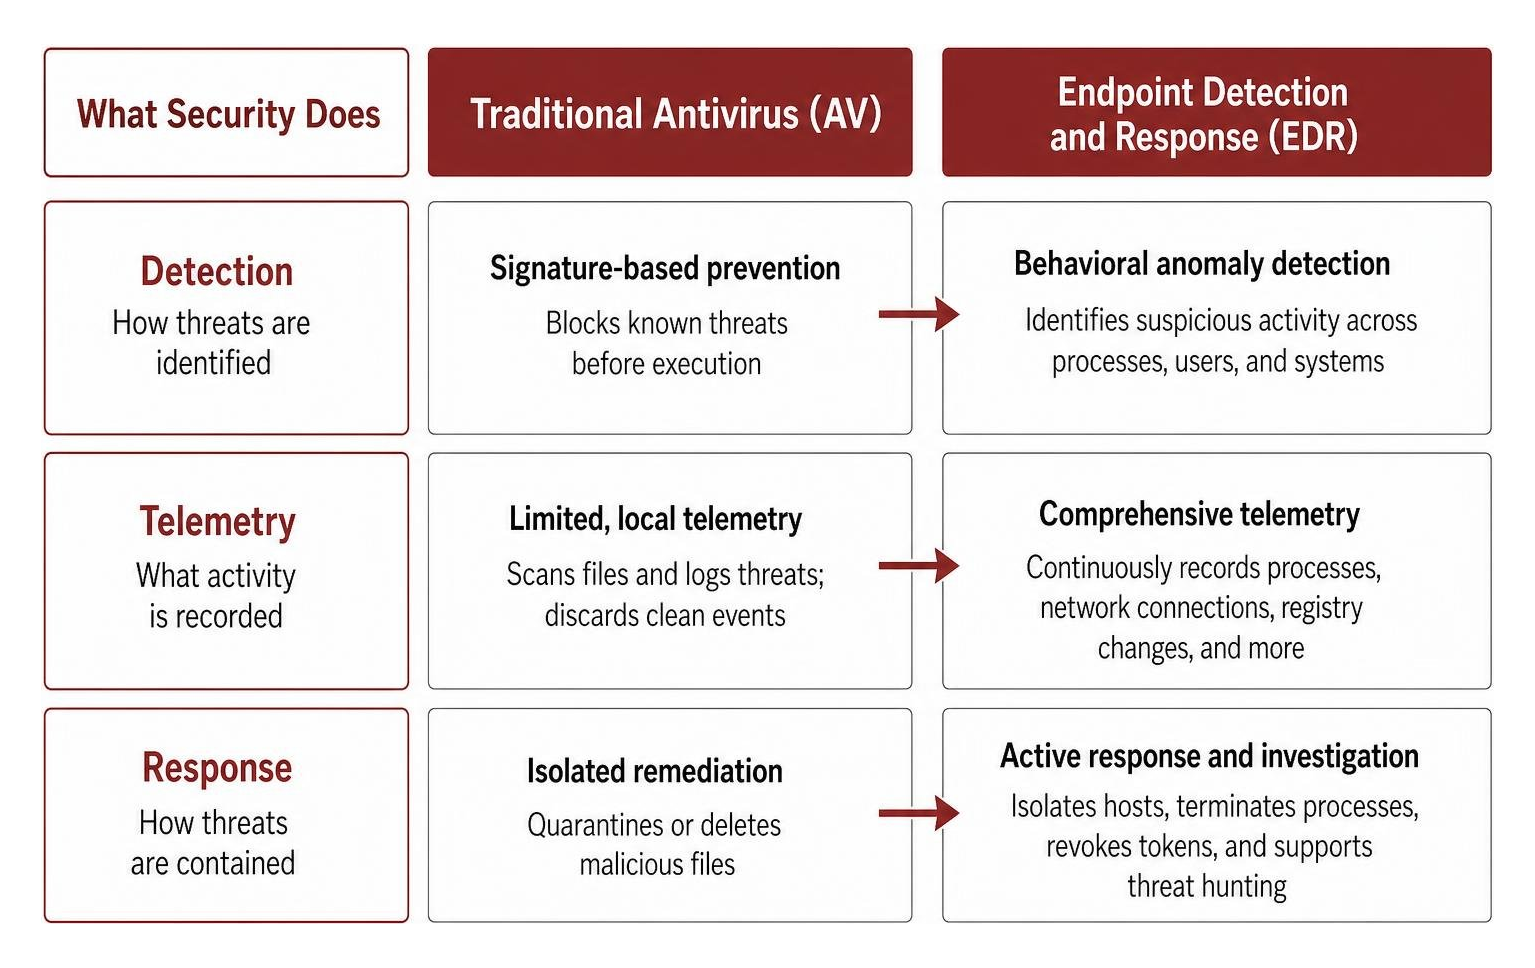
- Telemetry Retention: Traditional antivirus discards clean file events; advanced detection platforms continuously record process execution trees, parent-child process relationships, network sockets, and registry modifications.
- Adversary Containment: Beyond quarantining an individual file, detection platforms enable administrators to isolate a machine from the local network, kill active process trees, and revoke compromised authentication tokens.
- Threat Hunting: Security analysts can run queries across historical telemetry to identify subtle indicators of compromise (IOCs) that were not recognized as malicious when the initial connection occurred.
Preventive tools perform the necessary heavy lifting of stopping thousands of automated, opportunistic attacks every day. But when an adversary uses sophisticated evasion tactics, security operations require telemetry that extends well beyond local disk scans.
Building a Unified Security Strategy for Complete Visibility
Securing an enterprise requires evaluating infrastructure-specific requirements, regulatory obligations, and operational capabilities. Rather than managing disconnected point tools that create visibility silos, organizations benefit from a coordinated defense model that correlates telemetry across every layer of the technology environment.
For businesses seeking comprehensive coverage, DataEndure provides a continuum of capabilities, offering standalone Endpoint Protection, Managed Detection and Response (MDR), Extended Detection and Response (XDR), Open XDR, and Delta Detection & Response (DeltaDR).
DataEndure’s Delta Detection & Response (∆DR), also called DeltaDR, is a fully managed, unified Security-as-a-Service platform that combines a curated, composable security stack with a 24×7 team of security experts delivering continuous incident response. Operating as a white-labeled version of the WhiteDog cybersecurity platform, Delta Detection & Response has no comparable solution on the market.
Delta Detection & Response goes beyond traditional XDR frameworks by delivering layered defense across email, DNS, identity, endpoint, network, and cloud assets. This architecture integrates 24/7 security operations with Continuous Threat Exposure Management (CTEM) to continuously identify attack vectors and prioritize risk reduction. Key benefits of Delta Detection & Response include:
- Adaptive Multi-Layered Protection: Defenses evolve alongside emerging threats across endpoints, cloud workloads, and identity providers.
- Evergreen Technology Stack: The security stack updates continuously without forcing organizations through disruptive vendor migrations.
- Cross-Layer Telemetry Correlation: Alerts from identity stores, mail gateways, and endpoints are unified into high-fidelity incidents to accelerate triage.
- Faster Detection and Recovery: Continuous incident response workflows contain threats and guide remediation to restore normal business operations quickly.
- Scalable Delivery: Designed to protect environments scaling from 5 to 50,000 endpoints with flexible adoption options and rapid 30-day onboarding.
When evaluating endpoint technologies or architecting an enterprise-wide defense, security must be viewed as an enabler of business resilience. Preventing file execution at the host level is a foundational first step, but pairing layered endpoint controls with managed detection, cross-vector visibility, and continuous response helps your organization remain resilient against sophisticated modern threats.