Contact

DataEndure | Cybersecurity & IT Resilience Experts

Under Attack?
  • Services
    • Managed Services

      • Cloud Security
      • Email Security
      • Endpoint Security
      • Network Security
      • N-SOC

      Compliance

      • GRC
      • Readiness Assessments
      • Risk Management

      Complimentary Health Checks

      • Network Health Check
      • Resiliency Workshop
      • Security Health Check

      In-Depth Assessments

      • Application Dependency Mapping
      • CISO Assessment
      • Dark Data Assessment
      • Network Assessment
      • Penetration Testing

      Why Layered Defense is Critical

      Layered security is about protecting all vectors that have access into your network, and the network is no longer just inside your datacenter. It's wherever your endpoints, people, data, and assets reside.

      View the Video >>

  • Expertise
    • Security & Compliance

      • Layered Defense Strategy
      • Cyber Threats & Solutions

      Information Management

      • Data Resilience

      Cloud & Data Science

      • Digital Transformation

      Infrastructure

      • Scale and Efficiency

      Network

      • Network Resilience
      What does "good" cybersecurity look like?

      What does "Good" Cybersecurity look like?

      Discover key insights for robust cybersecurity, addressing critical gaps and navigating evolving threats.

      Read the Blog >>

  • Industries
  • Company
    • About Us

      • Leadership
      • News
      • In the Community
      • Careers
      • Contact Us

      Partners

      • Strategic Partners
      • Technology Partners
      • Partner Program
      securing data 40 years since 1984

      Leading the Way Through Change

      Explore over 40 years of industry leadership and lasting impact as we delve into the remarkable history of Data Endure. 

      Learn More >> 

  • Resources
    • Learn

      • Security Advisories
      • Blog
      • Case Studies
      • Podcast
      • Events
      • Videos
      • White Papers

      Connect

      • Contact Us
      • Newsletter Sign Up
      • Partner Program
      The AI Gold Rush: How to Build a Winning On-Prem Strategy

      Watch our Tech Talk Series

      Stay up to date on the latest in cybersecurity with our monthly Tech talk series.

      Watch the Series >>

Home > Network > Microsegmentation: Defense against unseen mines in your network

Microsegmentation: Defense against unseen mines in your network

October 31, 2022

Ross Rehart, Client Architect, Networking at DataEndure
Ross Rehart, MSc.

Client Architect, Networking

I proudly served in the US Navy for the better part of 14 years. The first ship I served on was the USS Missouri (BB-63) as a Hospital Corpsman. During my time aboard, we deployed to the Persian Gulf as part of the battle contingent for Operation Desert Storm.

Whenever a ship enters a potentially dangerous situation, the Captain orders, “General Quarters, set condition Zebra.” Condition Zebra means that every doorway on the ship is closed and ‘dogged shut.’ All Navy ships are equipped with doors that have a series of 10 – 16 latches around the parameter known as ‘dogs’ to ensure the ship’s watertight integrity should one section suffer battle damage. Essentially, we microsegment the ship to ensure we can continue our mission should one area become compromised.

While transiting into our battle area, knowing that the enemy had mined the waters, the Missouri took the lead into the straight as we were the most heavily armored ship in the battlegroup. As we were transiting the straight, two of the ships in our battlegroup (the USS Tripoli and USS Princeton) each struck a mine only a few hundred yards from our position. Setting condition Zebra saved the lives of the sailors on those ships and the ships themselves from sinking when they suddenly had a large hole in the side of the ship.
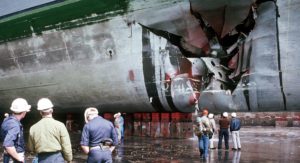
The USS Tripoli in dry dock in Bahrain for repairs after damaged by an Iraqi mine. February 1991.

Hidden mines are everywhere, many won’t know it until they’re hit.

So how do you plan to save your ‘ship’ from sinking? Networks and corporate infrastructures of today are not unlike any ship. There are many ‘compartments’ and vulnerable areas that hackers lay mines in just waiting to go off. Many enterprises still have their infrastructures built on architectures that were not designed for the challenges of today’s cyber threats. The hackers will get in if there is even a small hole in your ship. And if your doors aren’t dogged down, that is, the network properly secured and segmented, they will spread, sometimes causing irreparable damage. The cost to repair this damage can quickly run into tens of thousands of dollars, and the harm to the business could run into the millions. Additionally, the harm to your company’s reputation may end up costing the company thousands to millions of dollars in restitution, lost sales, etc.

Most network architects and engineers still build networks in very traditional ways. They use VLANs, VRFs, VPNs, firewall security contexts, etc. The problems with these types of architectures include high administrative overhead, complex network setups, vendor lock, and, quite often, compromising network security for its users’ convenience.

Today’s modern networks are built on software. Think of policy-driven infrastructure as code. Let’s use Zero Trust Networking (ZTN) as an example.

Companies implementing ZTN are forced to look at all communications on their networks. Which applications are communicating with databases, DNS, internet resources, etc.? Which users are communicating with applications? And which networks allow access to the applications? When they examine these points, they often find dozens, if not hundreds, of cases of unexpected or unauthorized access.

Once the applications are correctly mapped and validated, companies can now introduce microsegmentation via software (hardware agnostic). Microsegmentation (a.k.a. ZTN), by design, begins with the premise of implicit denial and then allows only necessary communications to happen. Therefore, if a hacker does get in, their ability to move laterally in the network is limited or completely cut off. In other words, the doors are dogged, and the ship is safe from additional damage or otherwise sinking.

DataEndure can help you on your journey to a safer network. If you’d like more information, reach out or read our whitepaper here.

Search

Blog Categories

  • Cloud & Data Science
  • Information Management
  • Infrastructure
  • Network
  • Podcasts
  • Security & Compliance
  • Security Advisories

Get started today!

We're here to help. Talk to us to learn more about how we can help your organization achieve digital resilience with solutions custom-built to meet the needs of your business.

SCHEDULE A MEETING

DataEndure
590 Laurelwood Drive
Santa Clara, CA 95054
800.969.4268

DataEndure © 2026. All Rights Reserved.  Privacy Policy

Follow Us

This website uses cookies to improve your experience. We'll assume you're ok with this, but you can opt-out if you wish. Accept Reject
Privacy & Cookies Policy

Privacy Overview

This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary
Always Enabled
Necessary cookies are absolutely essential for the website to function properly. This category only includes cookies that ensures basic functionalities and security features of the website. These cookies do not store any personal information.
Non-necessary
Any cookies that may not be particularly necessary for the website to function and is used specifically to collect user personal data via analytics, ads, other embedded contents are termed as non-necessary cookies. It is mandatory to procure user consent prior to running these cookies on your website.
SAVE & ACCEPT