Why Cyber Security Risks and Controls Define Your Organization’s Survival
Understanding cyber security risks and controls is a critical factor in determining how effectively an organization can recover from a security incident.
The average cost of a data breach hit USD 4.88 million in 2024, a 10% jump from the year before. Cybercrime continues to impact the global economy significantly, and human error remains a factor in 85% of incidents, highlighting that technology alone is not a complete solution.
Here is a quick-reference breakdown to orient you before we go deeper:
What is a cybersecurity risk? A cybersecurity risk is the potential for harm when a threat exploits a vulnerability in your systems, people, or data.
What is a cybersecurity control? A cybersecurity control is any measure — technical, procedural, or physical — that reduces the likelihood or impact of that risk materializing.
The three main categories of controls:
- People — security teams, training, executive buy-in
- Technology — firewalls, MFA, continuous monitoring, detection tools
- Data — accurate risk data, financial quantification, access governance
The most critical risks organizations face today:
- Identity-based attacks (30% of all intrusions)
- Ransomware and malware
- Phishing and social engineering
- Unpatched legacy systems
- Unsecured generative AI initiatives (only 24% are currently secured)
- Supply chain and third-party vulnerabilities
For IT leaders in regulated industries, managing these challenges involves navigating staff shortages, alert fatigue, and evolving compliance demands. The gap between available cybersecurity workers and open roles could reach 85 million by 2030. Organizations facing serious skills shortages often experience higher breach costs, emphasizing the importance of adequate staffing.
The objective is to build a connected, layered defense that identifies risk early, responds efficiently, and maintains business continuity without creating unnecessary operational complexity.
That is exactly what this guide covers.
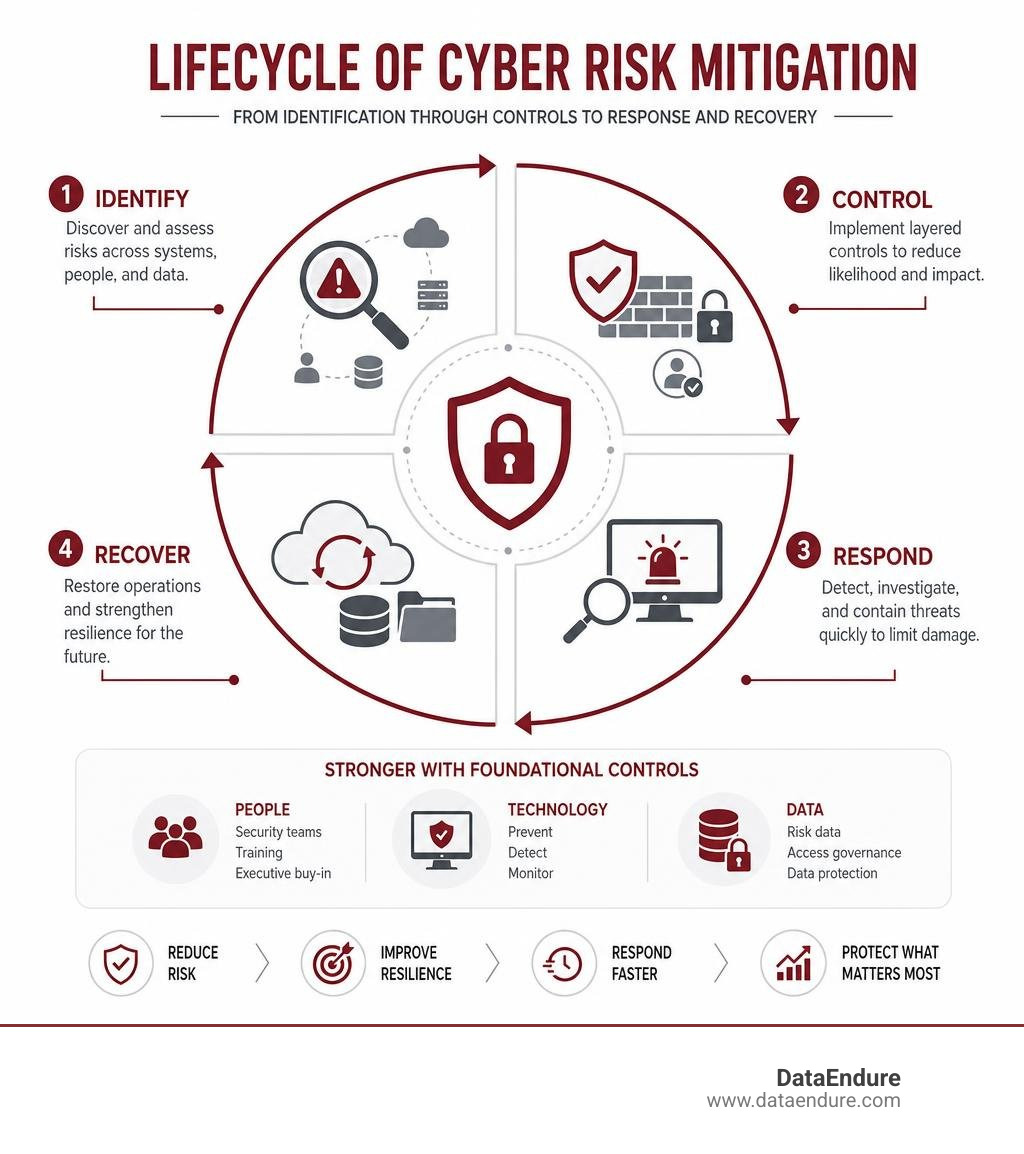
Defining the Landscape: Risk vs. Control
To successfully protect an enterprise, we must first establish a clear distinction between the problems we face (risks) and the tools we use to solve them (controls).
A cybersecurity risk is the mathematical intersection of a threat (an active bad actor, malware, or natural disaster), a vulnerability (a weakness in your system, process, or workforce), and an asset’s value. In simple terms: What could go wrong, how likely is it to happen, and how much will it hurt if it does?
A cybersecurity control, on the other hand, is the tactical shield. It is a process, policy, physical barrier, or software tool designed to block, detect, or recover from an exploit.
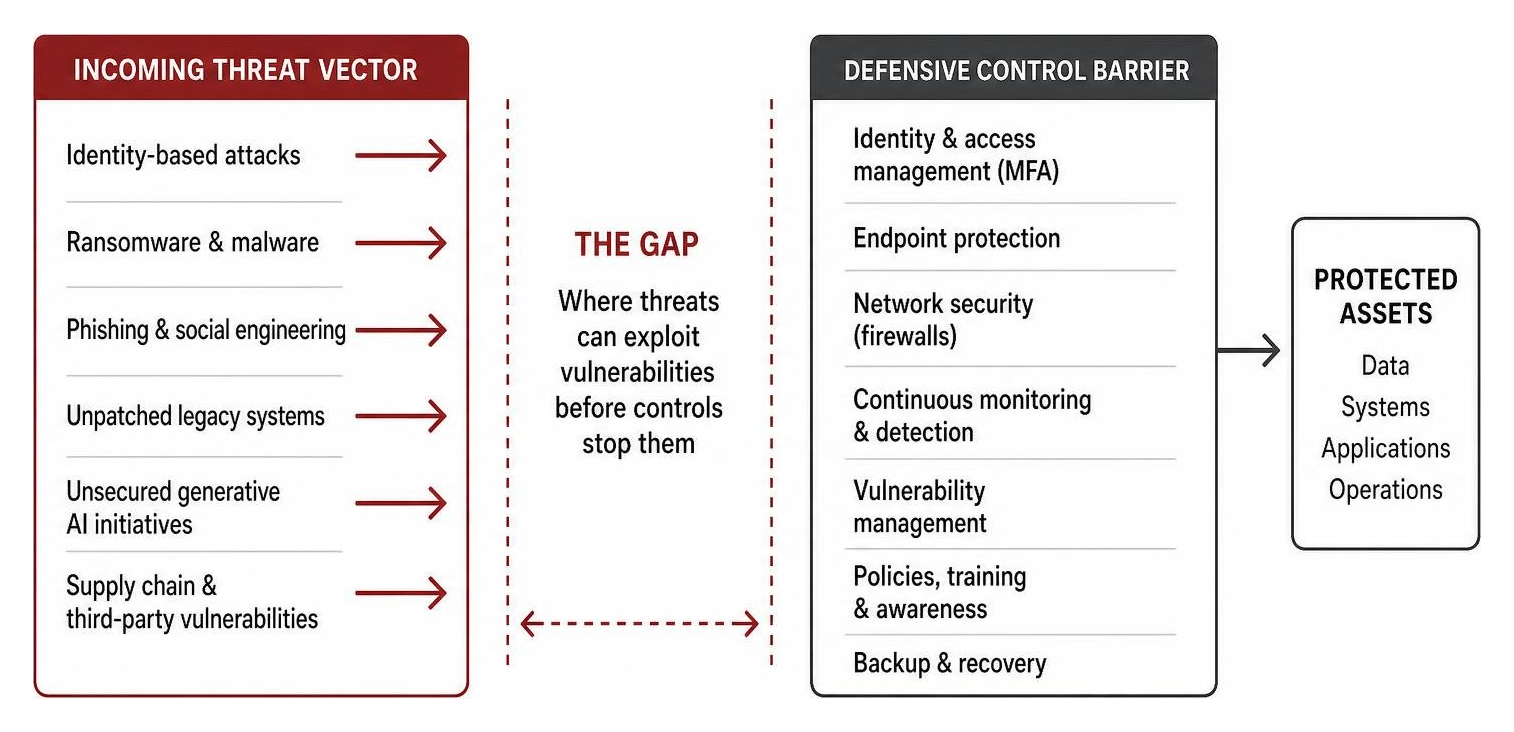
To help visualize how these two concepts interact, consider this comparative breakdown:
| Cybersecurity Risk (The Problem) | Cybersecurity Control (The Safeguard) |
|---|---|
| Credential Theft via Phishing: Attackers tricking employees into revealing login details. | Multifactor Authentication (MFA): Requiring a secondary verification code to block unauthorized access. |
| Ransomware Encryption: Malware locking critical operational databases. | Isolated Cloud Backups & EDR: Maintaining immutable copies of data and deploying endpoint detection to kill malicious processes. |
| Unpatched Software Vulnerabilities: Hackers exploiting known bugs in legacy operating systems. | Automated Patch Management: A structured schedule to test and deploy software updates within 72 hours of release. |
| Insider Data Exfiltration: Disgruntled employees or compromised accounts copying sensitive IP. | Data Loss Prevention (DLP): Restricting the transfer of classified files to external networks or USB drives. |
Understanding the Relationship Between Cyber Security Risks and Controls
We cannot implement controls in a vacuum. Every control deployed must map directly back to a validated risk.
When organizations suffer from “tool sprawl” — deploying dozens of disconnected security tools — it is usually because they bought software to solve immediate panic rather than systematic risk. This lack of alignment can create a high volume of false positives that increases alert fatigue for security teams.
To build a resilient architecture, organizations must balance threat exposure against their risk appetite. Risk appetite defines how much risk a business is willing to accept in pursuit of its strategic goals. For example, a financial technology firm will typically have a lower risk appetite for data exposure than a local retail brand.
By aligning controls directly with risk appetite, security functions as a business enabler rather than an operational bottleneck. To evaluate current defense postures against business objectives, organizations can leverage specialized security and compliance expertise to map out their specific risk profile.
The Three Pillars of Controls: People, Technology, and Data
A robust security posture is built on three core pillars. If any of these pillars are weak, the overall defensive structure is compromised:
- The People Pillar: Security is an organization-wide commitment. This pillar includes internal security engineering teams, executive leadership, and all employees handling corporate devices. Securing executive and board-level buy-in is essential for effective security performance management, ensuring the necessary resources and authority to maintain compliance.
- The Technology Pillar: This encompasses the automated tools that defend the perimeter and monitor the internal environment, such as firewalls, continuous attack surface monitoring, endpoint protection, and vendor access management. The key is integration—ensuring technology works as a unified ecosystem rather than isolated silos.
- The Data Pillar: Controls rely on the quality of the data driving them. This pillar focuses on gathering accurate, real-time risk data and converting technical vulnerabilities into financial risk quantification. Demonstrating the potential financial impact of a vulnerability helps transform security from an abstract technical expense into a concrete business decision.
For organizations balancing these pillars while navigating complex regulatory landscapes, integrating these elements is critical. Further details on aligning these pillars are available by exploring structured GRC strategies.
The Modern Threat Landscape: Common Cybersecurity Risks
The threats faced today are highly automated, targeted, and constantly evolving. Attackers frequently utilize stolen credentials or exploit the rapid adoption of new, unsecured technologies to gain access.
1. Identity-Based Attacks
Identity has become a primary security perimeter. Today, identity-based attacks make up 30% of all network intrusions, making compromised credentials a common entry point into corporate networks. Attackers use techniques like Kerberoasting to manipulate authentication protocols, hijack privileged service accounts, and move laterally through networks.
2. Ransomware and the Battle for Recovery
Ransomware remains a highly disruptive threat, with modern tactics often targeting backup systems to hinder recovery efforts. If backup infrastructure is not hardened and isolated, disaster recovery plans may fail to achieve their objectives. Industry data indicates that a significant portion of ransomware victims face repeat incidents if the root-cause vulnerabilities are not fully remediated during recovery.
3. The Generative AI Explosion
The rapid adoption of artificial intelligence has introduced new security considerations. Currently, only a minority of generative AI initiatives are fully secured, leaving organizations exposed to risks such as prompt injection attacks, where models are manipulated to leak proprietary data, and data poisoning, which can compromise decision-making tools.
For a deeper dive into how these threats operate and how to build defenses against them, resources such as this guide to common cyber threats offer further insights.
Industrial Control Systems (ICS) and Operational Technology (OT) Vulnerabilities
While standard IT security focuses primarily on protecting data confidentiality, Operational Technology (OT) and Industrial Control Systems (ICS) prioritize safety and continuous operational availability.
This sector is a frequent target, with manufacturing absorbing a significant portion of reported cyberattacks.
The unique risks facing OT environments include:
- Legacy System Vulnerabilities: Many industrial plants rely on legacy controllers that communicate using unencrypted protocols lacking built-in authentication.
- Insufficient Network Segmentation: Failing to separate corporate IT networks from physical plant floors can allow malware to cross over, potentially impacting physical operations.
- Cyber-Physical Convergence: Digital intrusions that manipulate physical processes can result in equipment damage and safety hazards.
To protect these environments, operators can follow the Purdue Model to isolate process-safety networks, enforce multi-factor authentication (MFA) on remote engineering sessions, and establish a dedicated industrial DMZ to broker cross-network communications.
Implementing Cyber Security Risks and Controls: A Strategic Framework
Deploying cybersecurity controls without a structured framework can lead to inefficient resource allocation and critical security gaps.
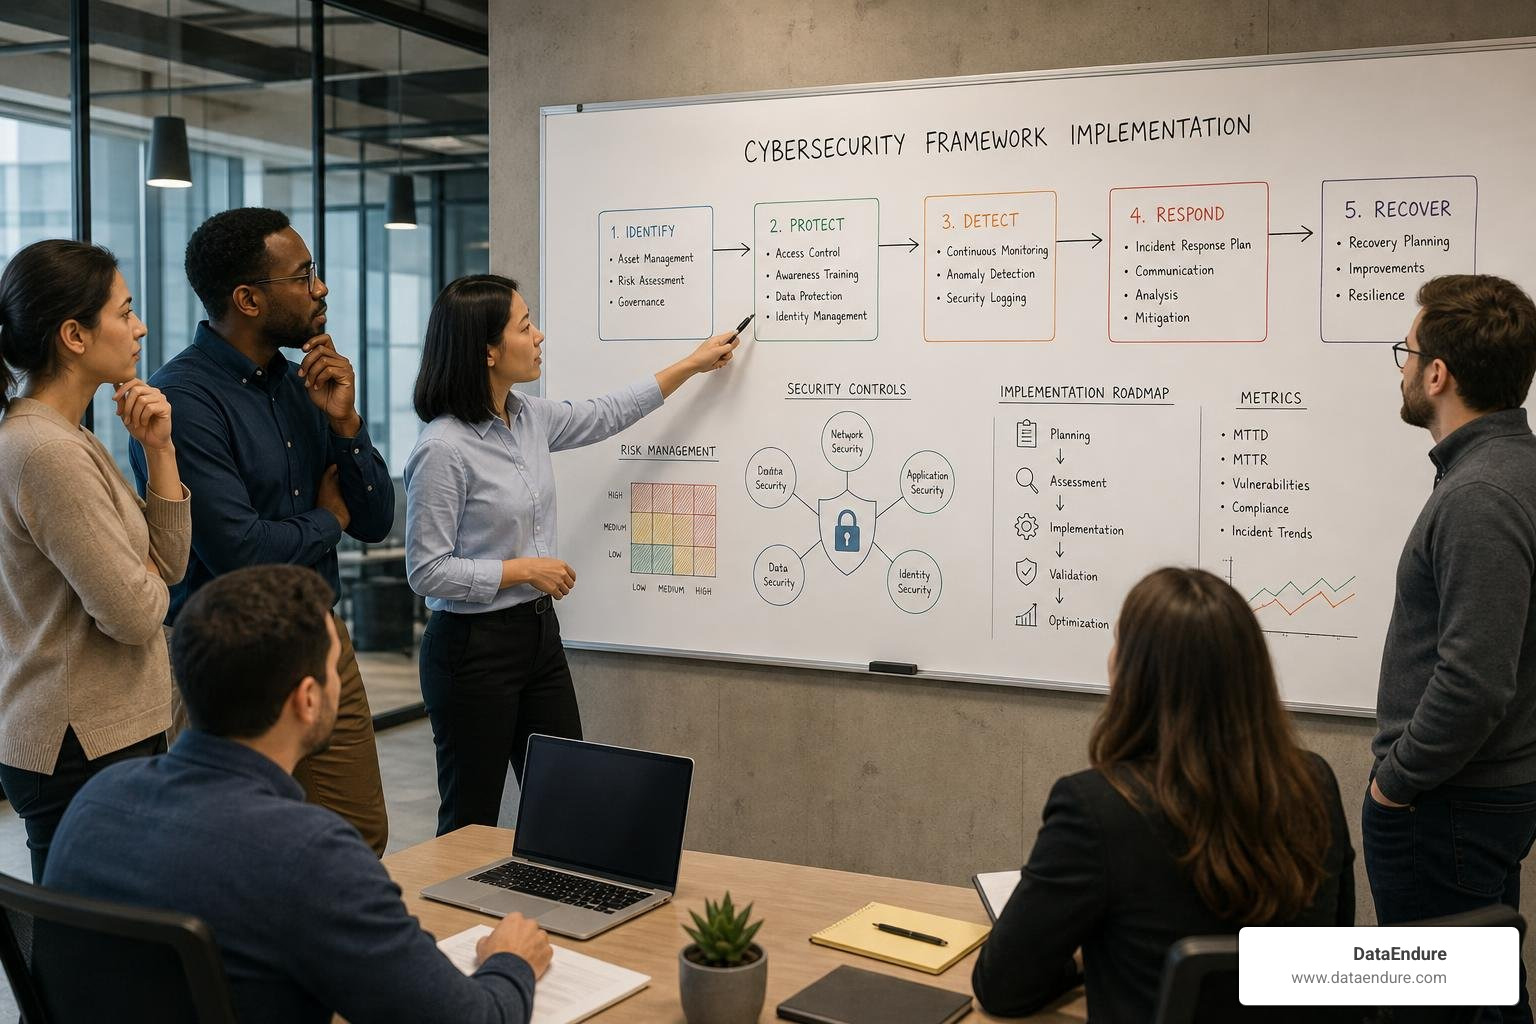
To build an efficient, defensible security program, a “framework-first” approach is highly effective. This methodology ensures that technical safeguards are mapped directly to established industry standards, helping organizations scale securely. This strategy is detailed further in this guide on a framework-first growth strategy.
How Frameworks Align Cyber Security Risks and Controls
The most effective way to organize defenses is to adopt a globally recognized framework, such as the NIST Cybersecurity Framework (CSF) 2.0 or the CIS Critical Security Controls.
The NIST CSF 2.0 organizes security operations into six core functions: Govern, Identify, Protect, Detect, Respond, and Recover. This structure ensures that risk management is treated as an enterprise-wide business strategy.
For organizations looking to build a tactical, prioritized defense, the CIS Controls offer a data-driven path. This framework defines 18 Critical Security Controls, scaled across three distinct Implementation Groups (IGs) to match resources and risk profiles:
- Implementation Group 1 (IG1): Represents “basic cyber hygiene,” establishing a foundational set of safeguards to defend against common, non-targeted cyberattacks.
- Implementation Group 2 (IG2): Designed for mid-market enterprises managing moderate risk and operational complexity.
- Implementation Group 3 (IG3): Tailored for large enterprises and highly regulated organizations facing sophisticated, targeted threats.
To understand how these controls map to global defense standards, organizations can review the technical specifications outlined in the ETSI Critical Security Controls for Effective Cyber Defence.
Furthermore, adhering to these frameworks supports compliance with evolving regulatory requirements. To ensure organizations stay ahead of these compliance mandates, resources like the 2026 Governance Risk Management Compliance Guide can provide structured guidance.
The Human Factor: Employee Training and Security Culture
Because human error is a factor in a significant majority of data breaches, employees represent a critical component of an organization’s defense strategy.
Rather than relying solely on annual training sessions, building a resilient security culture involves continuous, interactive engagement integrated into daily workflows:
- Continuous Phishing Simulations: Conducting realistic, non-punitive phishing tests helps employees recognize advanced social engineering tactics.
- Credential Hygiene: Providing password managers and mandating MFA helps mitigate risks associated with password reuse.
- Collaborative Security: IT and security teams can work together to ensure that security controls do not interfere with daily productivity, reducing the incentive for employees to use unsecured “shadow IT” tools.
To explore methods for transitioning an organization toward a collaborative, secure cultural model, refer to this analysis on evolving IT security together.
Prevention, Detection, and Response: Balancing the Control Lifecycle
An effective cybersecurity strategy requires a balanced distribution of controls across the entire attack lifecycle. Focusing solely on prevention can leave an organization with limited visibility if an intrusion occurs.
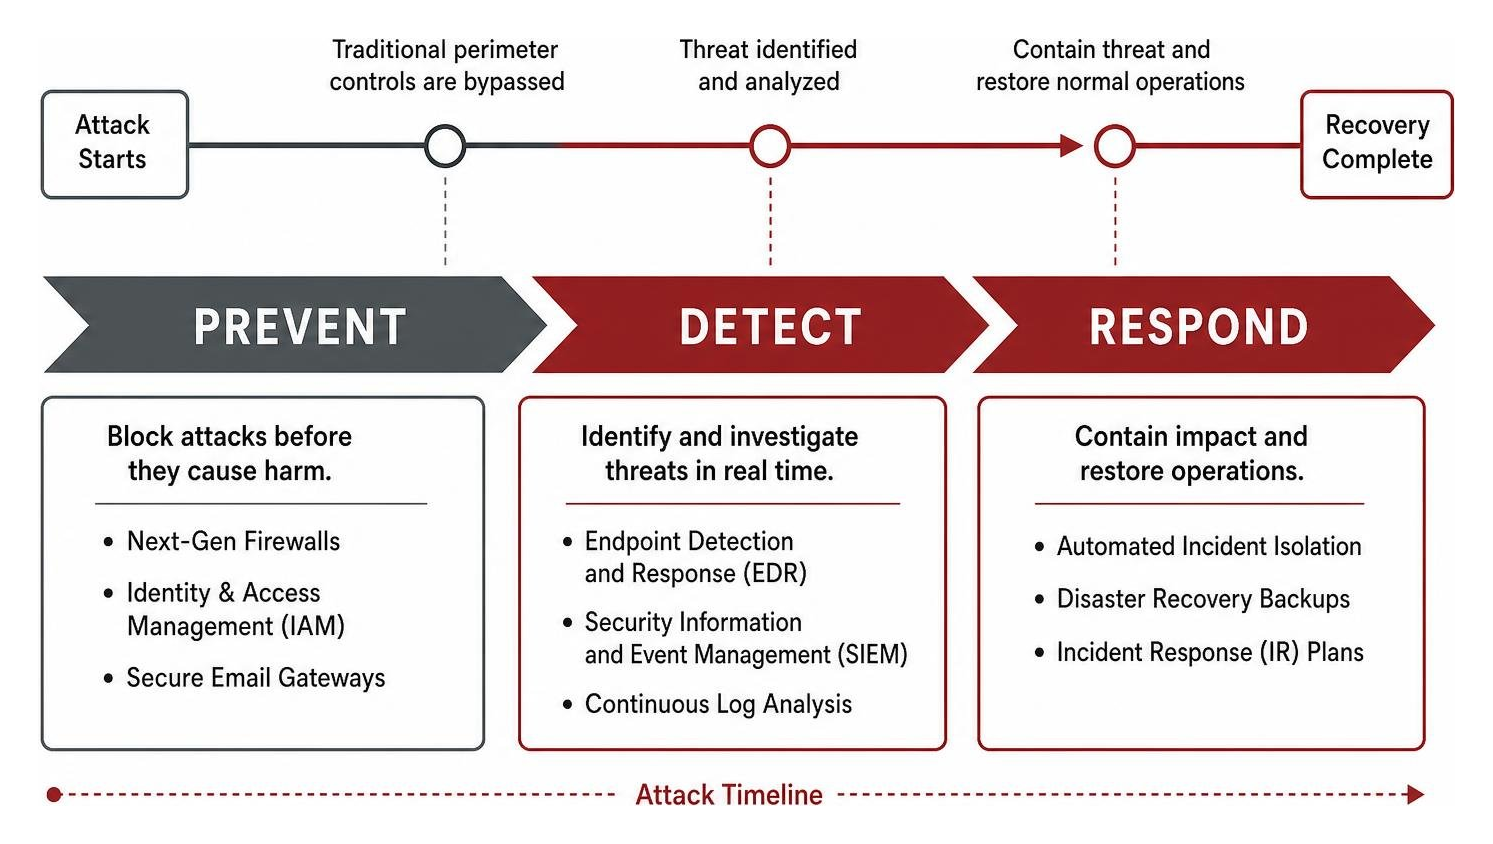
These controls are categorized into three distinct phases:
- Preventative Controls: Designed to block attacks before they cause harm, such as Next-Gen Firewalls, Identity and Access Management (IAM), and Secure Email Gateways.
- Detective Controls: Designed to identify active intrusions or system anomalies in real-time, such as Endpoint Detection and Response (EDR), Security Information and Event Management (SIEM), and continuous log analysis.
- Corrective/Response Controls: Designed to limit the damage of a successful exploit and restore systems to a secure state, such as automated incident isolation, disaster recovery backups, and formal Incident Response (IR) plans.
To build a balanced, resilient architecture, understanding how these components interlock is essential. The mechanics of these systems are explored in this guide to threat detection.
Measuring Control Effectiveness and Minimizing Dwell Time
A key metric in cybersecurity is dwell time—the period between an attacker’s initial entry and the detection of the intrusion. Minimizing this duration helps limit potential data exfiltration and operational impact.
To reduce dwell time, organizations can implement continuous monitoring and regular, independent control assessments:
- Continuous Security Monitoring: Centralizing and analyzing system event logs helps detect suspicious activity, such as privilege escalation, promptly.
- Independent Audits: Evaluating security operations against established frameworks provides valuable insights. Internal auditors can align assessments directly with the control frameworks used by IT and security teams. For detailed guidance on structuring these evaluations, refer to the Global Technology Audit Guide on Auditing Cybersecurity Operations.
- Managed Detection and Response (MDR): For organizations where building a 24/7 internal Security Operations Center (SOC) is not feasible, partnering with a Managed Detection and Response (MDR) provider can assist in detecting breaches, reducing alert noise, and accelerating response times.
To learn more about deploying managed detection and response services, refer to this expert managed detection guide.
Frequently Asked Questions about Cybersecurity Risks and Controls
What is basic cyber hygiene for modern enterprises?
Basic cyber hygiene is represented by Implementation Group 1 (IG1) of the CIS Controls. It consists of foundational safeguards that every organization should apply to protect against common, opportunistic attacks. Key steps include establishing an accurate inventory of all physical and software assets, enforcing multi-factor authentication (MFA) on all administrative and user accounts, maintaining isolated, regular data backups, and ensuring continuous patch management for all operating systems and applications.
How do boards oversee cybersecurity risk in 2026?
In July 2026, cybersecurity is recognized as a core fiduciary responsibility and strategic business priority rather than just an IT issue. Boards must treat cyber risk as an enterprise-wide risk within their Enterprise Risk Management (ERM) framework. This involves guiding management to model the financial implications of potential cyber incidents, establishing clear board-level oversight structures, and ensuring direct access to cybersecurity expertise. For a comprehensive framework on board-level cyber governance, directors should consult the 2026 Director’s Handbook on Cyber-Risk Oversight.
Why is network segmentation critical for OT security?
Network segmentation is critical because it prevents lateral movement. If an attacker compromises a computer in the corporate IT network (for example, through a phishing email), a lack of segmentation allows them to move freely into the physical plant floor. By carving the control environment into discrete zones separated by firewalls and unidirectional gateways—and strictly controlling traffic through an industrial DMZ—you ensure that an IT breach cannot cross over to disrupt physical manufacturing operations or compromise process safety.
Conclusion: Building Digital Resilience
Managing cyber security risks and controls is not about achieving absolute, impenetrable security—it is about building digital resilience. It is about ensuring that when a disruption occurs, an organization has the visibility, expertise, and architecture to isolate the threat and continue operating without significant impact.
Achieving this resilience requires a balanced, simplified approach to security architecture. Rather than increasing tool complexity, organizations benefit from curated, layered solutions that function as a unified ecosystem. Utilizing vendor-agnostic frameworks and integrated technologies helps deliver optimal business outcomes tailored to specific operational environments.
Effective risk management strategies should focus on:
- Rapid Detection: Monitoring environments continuously to identify and isolate active threats before they cause widespread damage.
- Alert Optimization: Filtering out false positives to allow internal IT teams to focus on strategic initiatives.
- Efficient Deployment: Designing and operationalizing critical security controls systematically.
By addressing talent shortages, legacy systems, and tool sprawl through structured frameworks, organizations can fortify their defenses and secure business continuity. For further guidance on establishing a simplified, highly resilient security posture, organizations can explore comprehensive risk management solutions.