The Evolution and Core Challenges of Threat Detection Automation
Understanding what threat detection in cybersecurity entails starts with recognizing the limitations of legacy tools. For decades, security operations centers (SOCs) have relied heavily on manual processes to monitor networks and parse threat feeds.
As attack velocity accelerates, human analysts face a high volume of unstructured Cyber Threat Intelligence (CTI) reports, blog posts, and vulnerability disclosures. With many breaches exploiting known vulnerabilities that remain unpatched, relying entirely on manual workflows creates persistent operational delays for security operations.
Traditional Signature-Based IDS Bottlenecks
Intrusion Detection Systems (IDS) rely on distinct indicators, such as network inspection rules or host memory and file signatures, to identify malicious behaviors. However, generating these signatures manually introduces notable bottlenecks:
- Manual Effort and Slow Adaptation: Converting raw CTI into high-precision detection logic requires extensive domain expertise. By the time an analyst manually extracts indicators and authors a rule, adversaries have often modified their tactics.
- Rule Bloat: Adding new rules for every newly disclosed indicator without auditing existing detection logic leads to massive rule bases. Rule bloat degrades computational performance, increases search latency, and strains network resources.
- Zero-Day Vulnerability Adaptation: Traditional signature creation relies on post-incident analysis, leaving security teams unprepared for fast-moving exploits.
Without automated assistance, security engineering teams spend considerable time maintaining legacy detection logic rather than proactively hunting for unseen threats. To dive deeper into modern enterprise strategies, explore The Complete Guide to Enterprise Breach Detection.
How Automation Solves Rule Bloat and Adaptation Delays
Automated threat detection automation addresses these legacy bottlenecks by replacing manual rule creation with continuous, intelligent reconciliation workflows. Instead of creating redundant rules, modern automated systems retrieve currently deployed rule bases, perform context matching, and evaluate whether to update an existing rule or author a net-new rule.

| Workflow Aspect | Traditional Manual Rule Generation | Automated AI Rule Generation |
|---|---|---|
| CTI Processing Speed | Hours to days per intelligence report | Seconds to minutes via LLM extraction |
| Rule Reconciliation | Manual review; frequently leads to duplicates | Automated context matching and deduplication |
| Engine Performance Impact | High risk of rule bloat and network latency | Low risk; rules are pre-profiled for execution efficiency |
| Adaptation Speed | Reactive; delayed behind active attack campaigns | Rapid; continuously synchronized with modern threat feeds |
By dynamically updating existing logic rather than continuously piling on single-use signatures, automation prevents database bloat while drastically reducing SOC operational overhead. Organizations seeking to streamline their daily SOC alerting load can learn more in A Practical Guide to Alert Fatigue Management Tools.
Autonomous CTI Mining and AI-Driven IDS Rule Generation
The emergence of Large Language Models (LLMs) and agentic AI security frameworks has opened new frontiers in CTI mining. Rather than relying on simple pattern matching, agentic frameworks analyze complex, unstructured threat reports, isolate relevant Tactics, Techniques, and Procedures (TTPs), and automatically translate those insights into executable detection code.
A prominent example of this advancement is detailed in the FALCON Research Paper on Autonomous CTI Mining. Agentic architectures decompose CTI mining into coordinated tasks: threat parsing, rule synthesis, syntactic validation, and functional verification.
Evaluating AI Frameworks for Threat Detection Automation
Agentic frameworks demonstrate high precision when generating complex detection logic across multiple detection syntaxes. For instance, empirical research on the FALCON framework demonstrates an average accuracy of 95% in automated IDS rule generation across network inspection and host-based signature formats.
Furthermore, qualitative evaluation by expert cybersecurity analysts yielded an 84% inter-rater agreement across key validation metrics, proving that agentic frameworks produce rules aligned with real-world security standards. This technology was highlighted during industry discussions at the Official Cybersecurity Summit Silicon Valley, emphasizing how autonomous CTI mining empowers defenders to stay ahead of active adversaries.
CTI-Rule Semantic Scoring vs Traditional NLP Metrics
Evaluating AI-generated code presents unique challenges. Standard Natural Language Processing (NLP) metrics like BLEU, ROUGE, or traditional RAGAS and BERT-F1 metrics evaluate word-level or surface-level similarities. However, these metrics fail when applied to technical cybersecurity rules:
- Syntax Sensitivity: An IDS rule can be functionally perfect while using completely different field structures or variables than a reference string, causing standard NLP metrics to score it poorly.
- Structural Gap: Raw CTI consists of verbose human language, whereas detection rules consist of strict, highly condensed domain logic, such as payload parameters, byte sequences, or event correlation criteria.
To overcome this, cutting-edge frameworks employ a specialized CTI-Rule Semantic Scorer. Utilizing fine-tuned Bi-encoder models trained specifically on cybersecurity domain data, the semantic scorer maps unstructured CTI and structured detection rules into a shared embedding space. This measures true functional alignment, ensuring the generated rule actually detects the specific threat behavior described in the intelligence report.
Multi-Format Detection Databases and Gap Analysis Tools
While automated rule generation creates new signatures, effective security operations also require immediate access to established detection logic across enterprise environments. Modern enterprise architectures span multiple platforms, demanding a unified schema for detection engineering.
Leveraging Unified Rule Engines and MCP Interfaces
To simplify detection engineering across fragmented SIEM query languages, tools like the Security Detections MCP Repository leverage the Model Context Protocol (MCP) to provide AI agents with standardized access to massive detection rule repositories.
The Security Detections MCP integrates over 8,200+ indexed detection rules spanning six core security detection categories:
- Platform-Agnostic Detection Logic: ~3,200+ reusable detection rules
- Detection Search Content: ~2,000+ detection searches
- Pre-Built Security Analytics: ~1,500+ detection rules
- Email Security Detection Logic: ~900+ email security rules
- Cloud and SIEM Query Logic: ~420+ security queries
- Large-Scale Log Query Logic: ~139+ log-scale queries
With access to 25 read-only tools that stay synchronized with detection content, AI agents can query existing rule repositories using token-optimized prompts. This allows security engines to identify existing coverage instantly, preventing duplicate rule generation and closing tool sprawl gaps across the enterprise.
MITRE ATT&CK Mapping and Threat Actor Coverage
A critical benefit of integrating unified detection engines with structured STIX data is automated coverage analysis. For example, the Security Detections MCP index maps:
- 172 threat actors
- 784 security software entities
- 4,362 actor-technique relationships
By linking threat actor profiles with specific MITRE ATT&CK techniques, automated tools extract behavioral procedure clusters to reveal exact coverage blind spots. If a newly emerging threat group targets an enterprise’s industry sector, an automated agentic pipeline can immediately identify missing detection logic and trigger autonomous rule generation to plug the gap.
Architectural Criteria for Evaluating Automated Solutions
When evaluating threat detection automation solutions, technical leaders must look beyond raw AI generation capabilities and examine the underlying validation architecture.
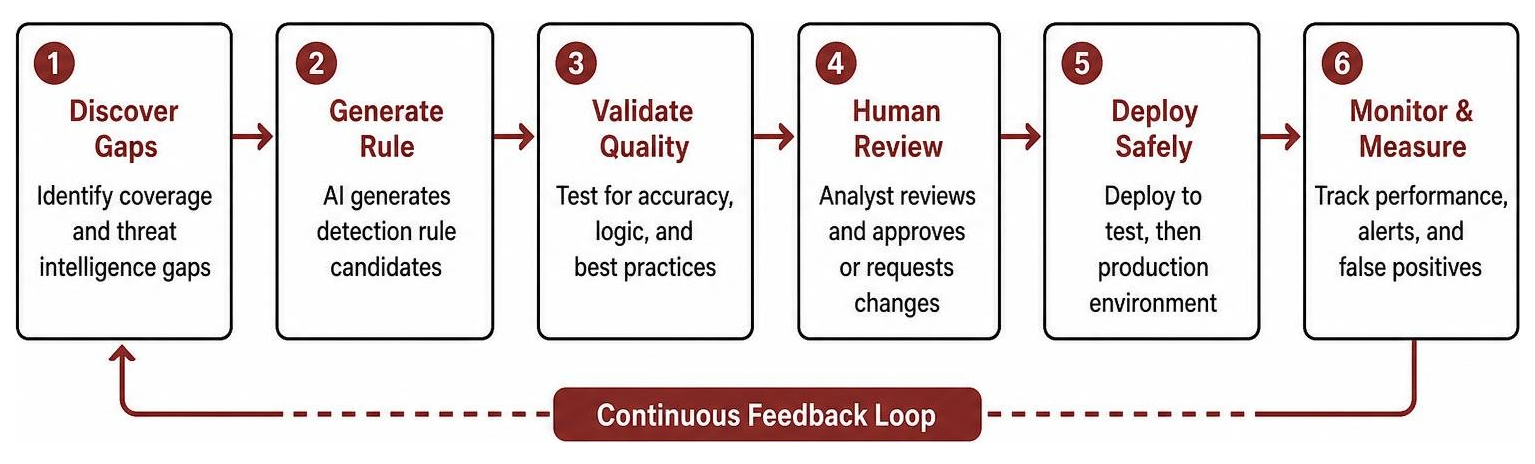
Integrating Threat Detection Automation into SOC Workflows
Automation should augment human expertise, not operate as an unmonitored black box. High-performing security architectures incorporate human-in-the-loop (HITL) authorization checkpoints before deploying generated rules to live production systems.
By connecting automated rule generation pipelines with Security Orchestration, Automation, and Response (SOAR) workflows, organizations can safely test, approve, and push updated signatures across security fabrics. For key considerations on evaluating SOAR integration, review our guide on SOAR and Your Security Posture.
Continuous Validation Pipeline: Syntax, Semantics, and Performance
To guarantee operational stability, an automated threat detection framework must execute a multi-stage validation loop before presenting rules to analysts:
- Syntax Verification: Rules are compiled against native engine parsers to confirm clean syntax without fatal errors.
- Semantic Alignment: The rule is evaluated via a Bi-encoder semantic scorer to verify that it accurately matches the target threat logic in the raw CTI report.
- Execution Profiling: The rule is run against simulated baseline network traffic or host file systems to measure performance overhead, CPU utilization, and potential false-positive rates.
If a rule fails any validation stage, self-correcting feedback loops pass the execution errors back to the generating agent, which iterates and fixes the code automatically. To learn more about built-in validation features, explore the Essential Features in a Complete XDR Solution.
Frequently Asked Questions
How do LLMs convert unstructured CTI reports into executable IDS rules?
Agentic AI frameworks use specialized prompt pipelines to parse raw CTI reports, identifying key indicators of compromise (IOCs) and behavioral patterns. The LLM then maps these extracted elements into domain-specific detection syntaxes, such as network inspection rules or host memory signatures, before running them through automated compiler checks.
What is the difference between CTI-Rule Semantic Scoring and standard metrics like BLEU or BERT-F1?
Standard metrics like BLEU or BERT-F1 measure literal string overlap or general textual similarity, which fails when evaluating structured code against conversational text. CTI-Rule Semantic Scoring uses a domain-specific Bi-encoder model trained to understand the underlying functional relationship between unstructured cybersecurity threat descriptions and technical detection syntax.
How does Model Context Protocol improve detection engineering across multiple SIEM languages?
Model Context Protocol (MCP) provides a standardized interface that allows language models to interact seamlessly with multi-format detection databases. Rather than querying different SIEM languages independently, an MCP server provides unified tools to search, translate, and perform gap analysis across platform-agnostic rules, SIEM searches, email security logic, endpoint telemetry queries, and large-scale log analytics formats.
Conclusion
As modern attack vectors evolve across global networks, threat detection automation has become an important component of modern security architecture. Moving away from strictly manual rule generation helps security teams address rule bloat, operational overhead, and potential coverage gaps. Achieving durable security resilience requires pairing intelligent automated capabilities with structured operational workflows.
Modernizing security operations involves aligning automated rule generation, continuous validation, and comprehensive threat intelligence integration across multi-layered enterprise environments. By establishing resilient frameworks that combine automated parsing with rigorous testing, organizations can enhance detection accuracy and streamline SOC response processes.
To learn more about streamlining security operations and modernizing SOC capabilities, explore available Managed SOC and Breach Detection Services.